

Więcej o książce
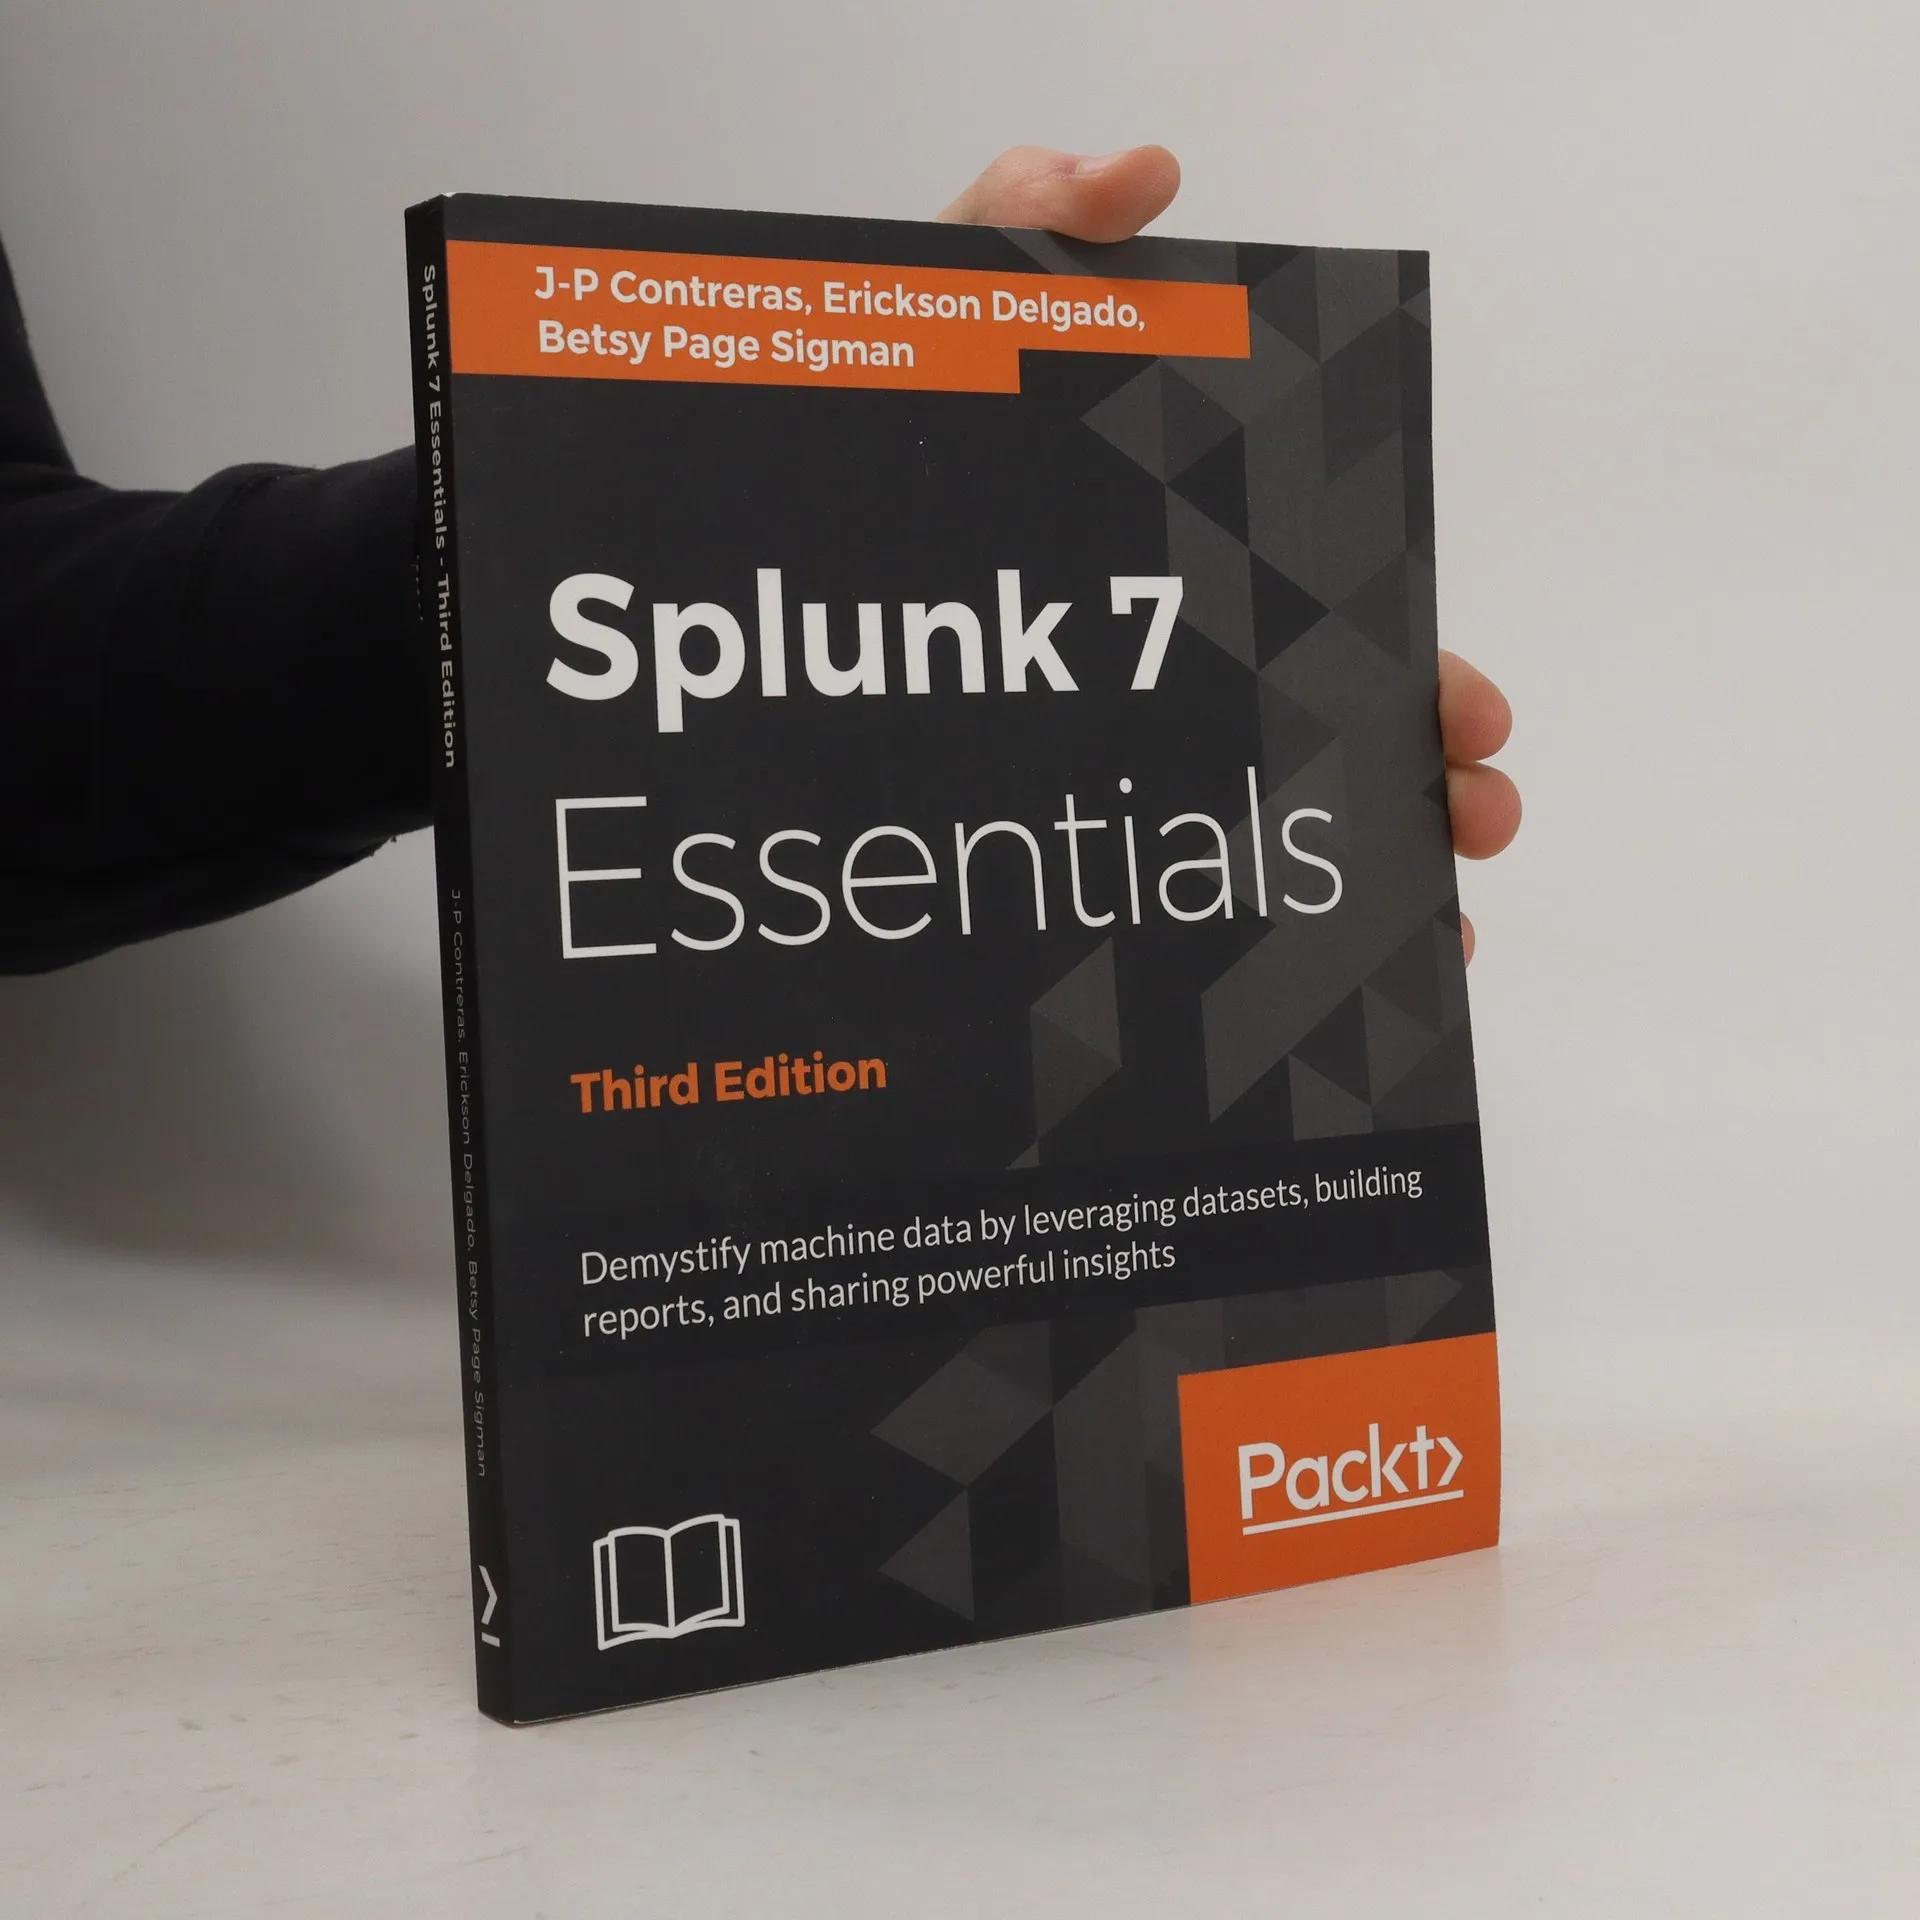
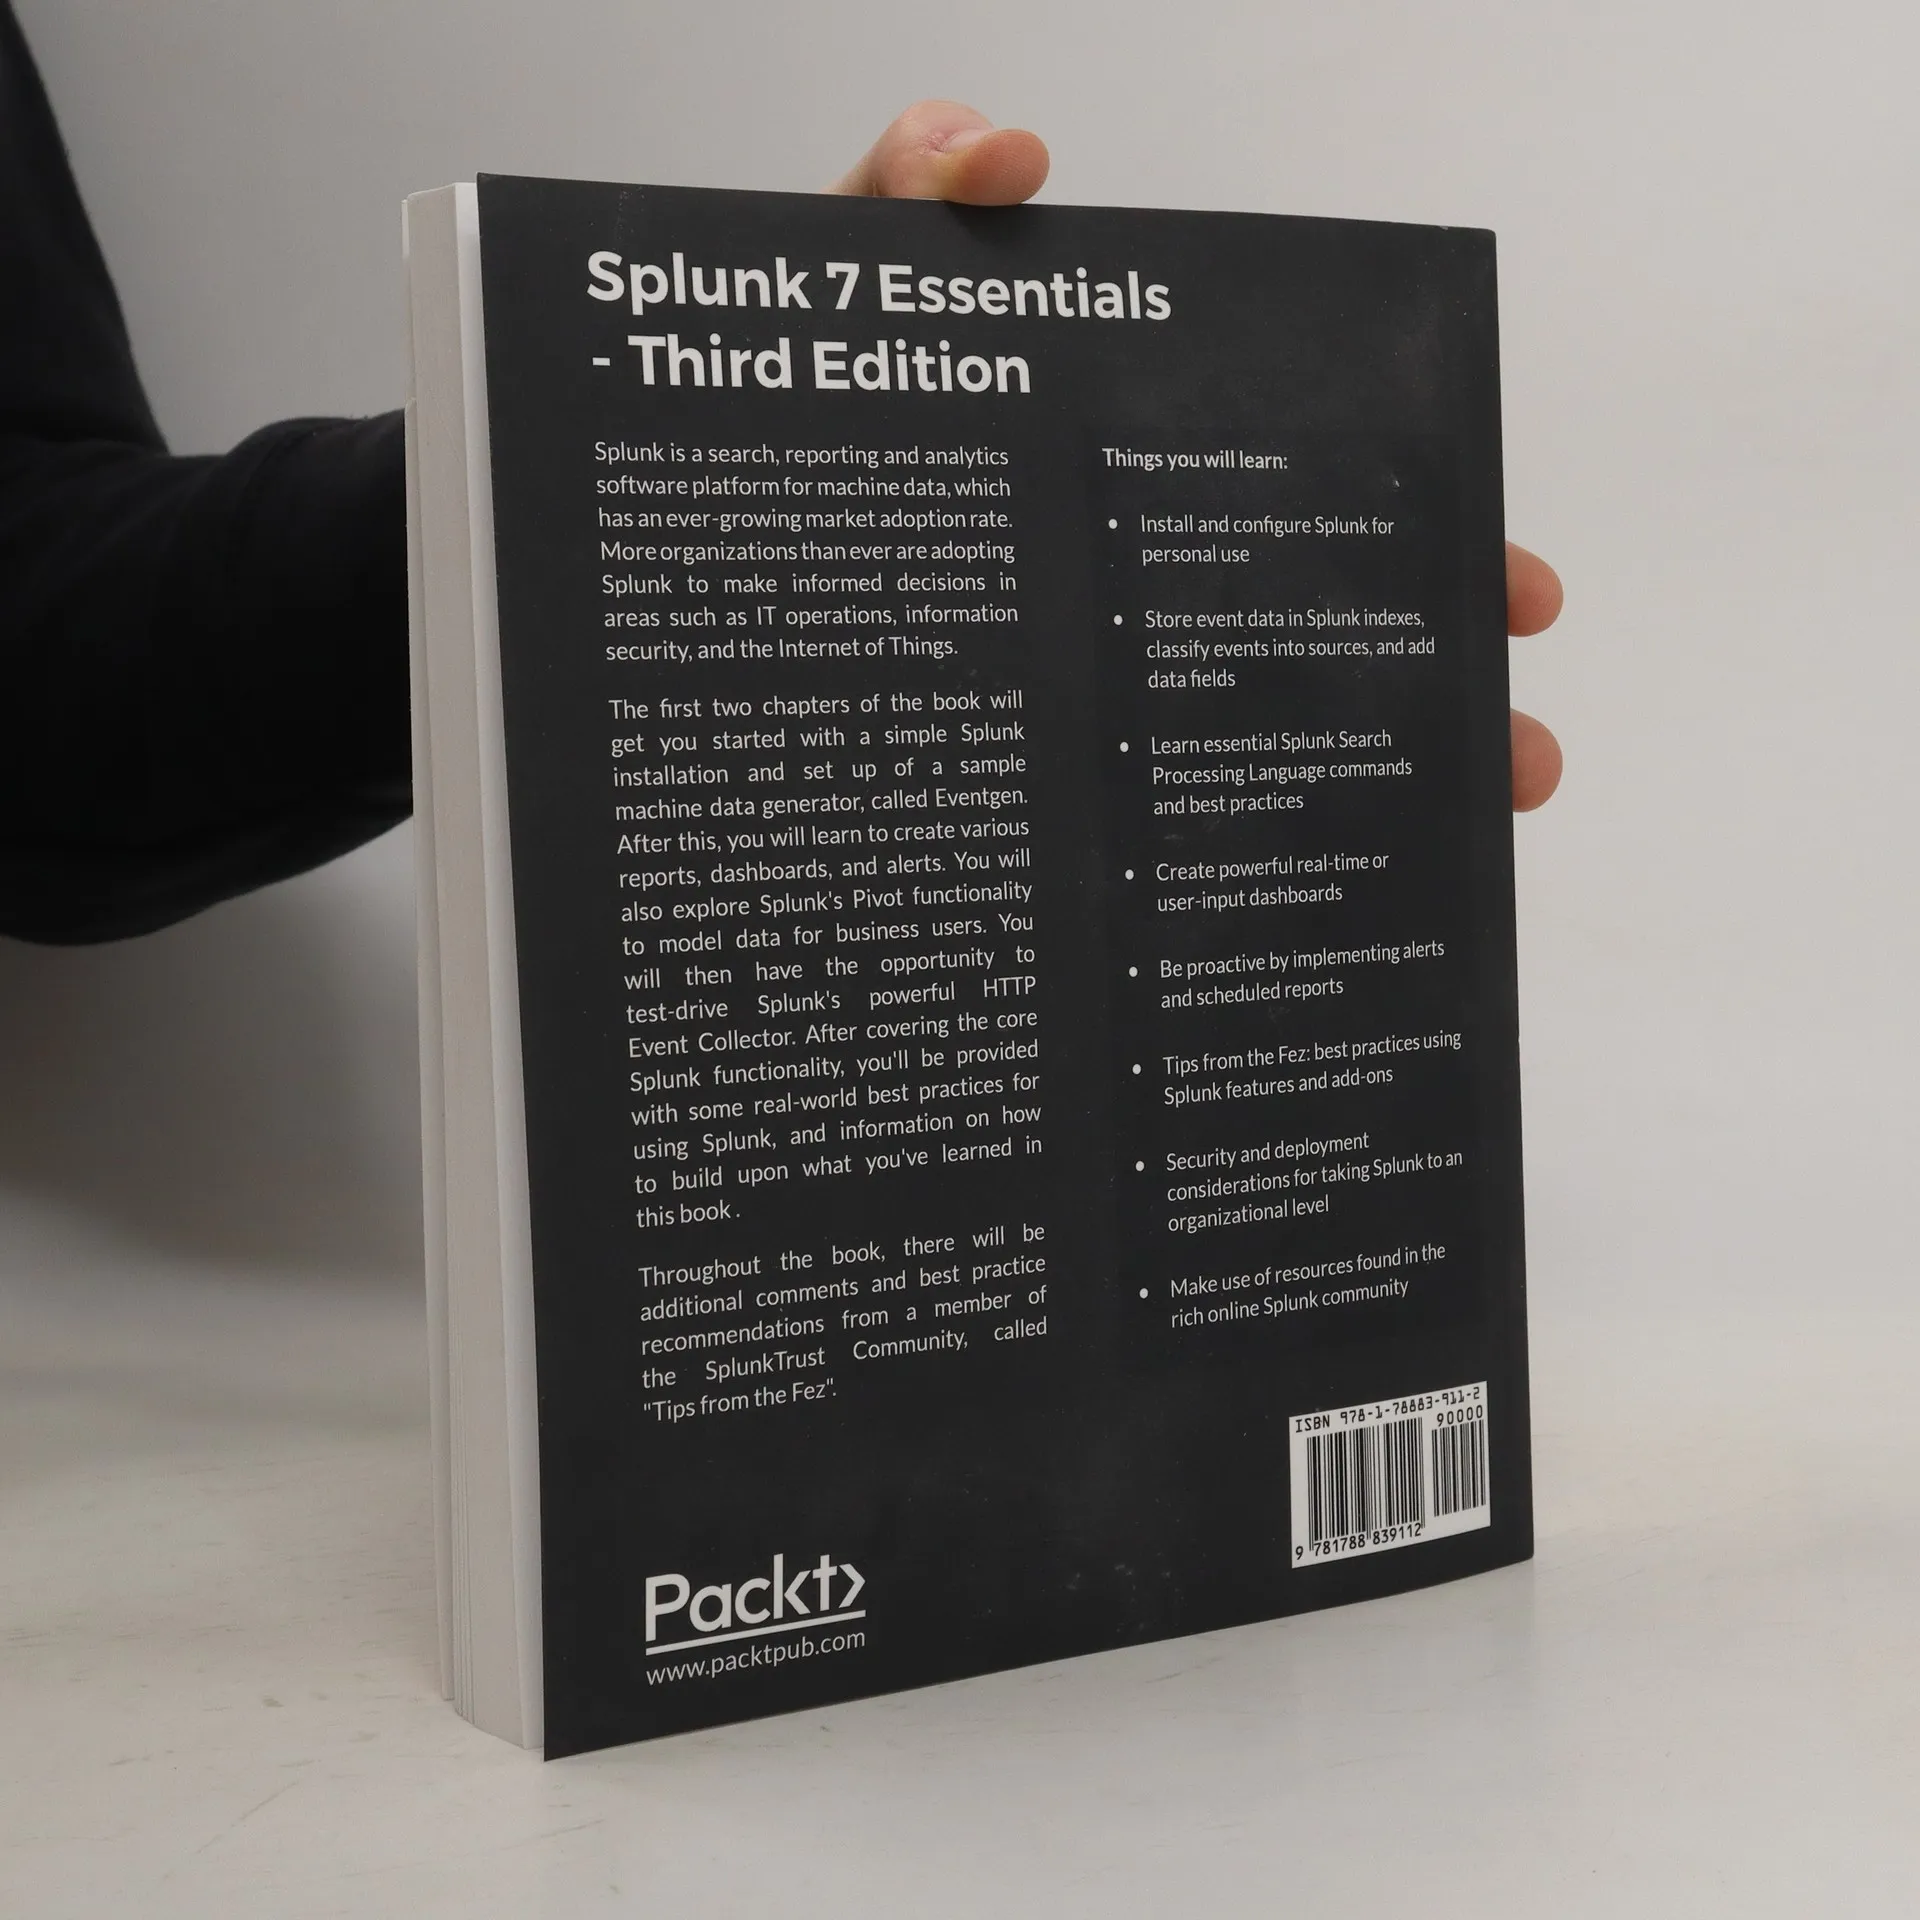
Splunk is a search, reporting and analytics software platform for machine data, which has an ever-growing market adoption rate. More organizations than ever are adopting Splunk to make informed decisions in such areas as IT Operations, Information Security and the Internet of Things. This book is for anyone who needs to get reports and analytics from machine data. The first two chapters of the book will quickly get you started with a simple Splunk installation and set up of a sample machine data generator, called Eventgen. You will then learn about searching machine data and enriching it with additional fields to provide analytical value. After this, you will learn to create various reports, dashboards, and alerts. You will also explore Splunk's Pivot functionality to model data for business users,who can then create visualizations with point and click ease. You will also have the opportunity to test drive Splunk's powerful HTTP Event Collector. After covering the core Splunk functionality, you'll be provided with some real-world best practices in using Splunk, and information on how to build upon what you've learned in this book to take Splunk to your organization. Throughout the book, there will be additional comments and best practice recommendations from a member of the Splunk Trust community, called "Tips from the Fez". Splunk Trust is a Splunk-sponsored community of the top Splunk talent in the marketplace
Zakup książki
Splunk 7 Essentials - Third Edition, J-P Contreras, Steven Koelpin, Erickson Delgado
- Język

- Rok wydania
- 2018
- Oprawa
- (miękka)
Metody płatności
Brakuje nam tutaj Twojej recenzji.
- Tytuł
- Splunk 7 Essentials - Third Edition
- Język
- angielski
- Autorzy
- J-P Contreras, Steven Koelpin, Erickson Delgado
- Wydawca
- Packt Publishing
- Rok wydania
- 2018
- Oprawa
- miękka
- Liczba stron
- 220
- ISBN10
- 1788839110
- ISBN13
- 9781788839112
- Seria
- Tagi
- Ocena
- 4 z 5
- Opis
- Splunk is a search, reporting and analytics software platform for machine data, which has an ever-growing market adoption rate. More organizations than ever are adopting Splunk to make informed decisions in such areas as IT Operations, Information Security and the Internet of Things. This book is for anyone who needs to get reports and analytics from machine data. The first two chapters of the book will quickly get you started with a simple Splunk installation and set up of a sample machine data generator, called Eventgen. You will then learn about searching machine data and enriching it with additional fields to provide analytical value. After this, you will learn to create various reports, dashboards, and alerts. You will also explore Splunk's Pivot functionality to model data for business users,who can then create visualizations with point and click ease. You will also have the opportunity to test drive Splunk's powerful HTTP Event Collector. After covering the core Splunk functionality, you'll be provided with some real-world best practices in using Splunk, and information on how to build upon what you've learned in this book to take Splunk to your organization. Throughout the book, there will be additional comments and best practice recommendations from a member of the Splunk Trust community, called "Tips from the Fez". Splunk Trust is a Splunk-sponsored community of the top Splunk talent in the marketplace