

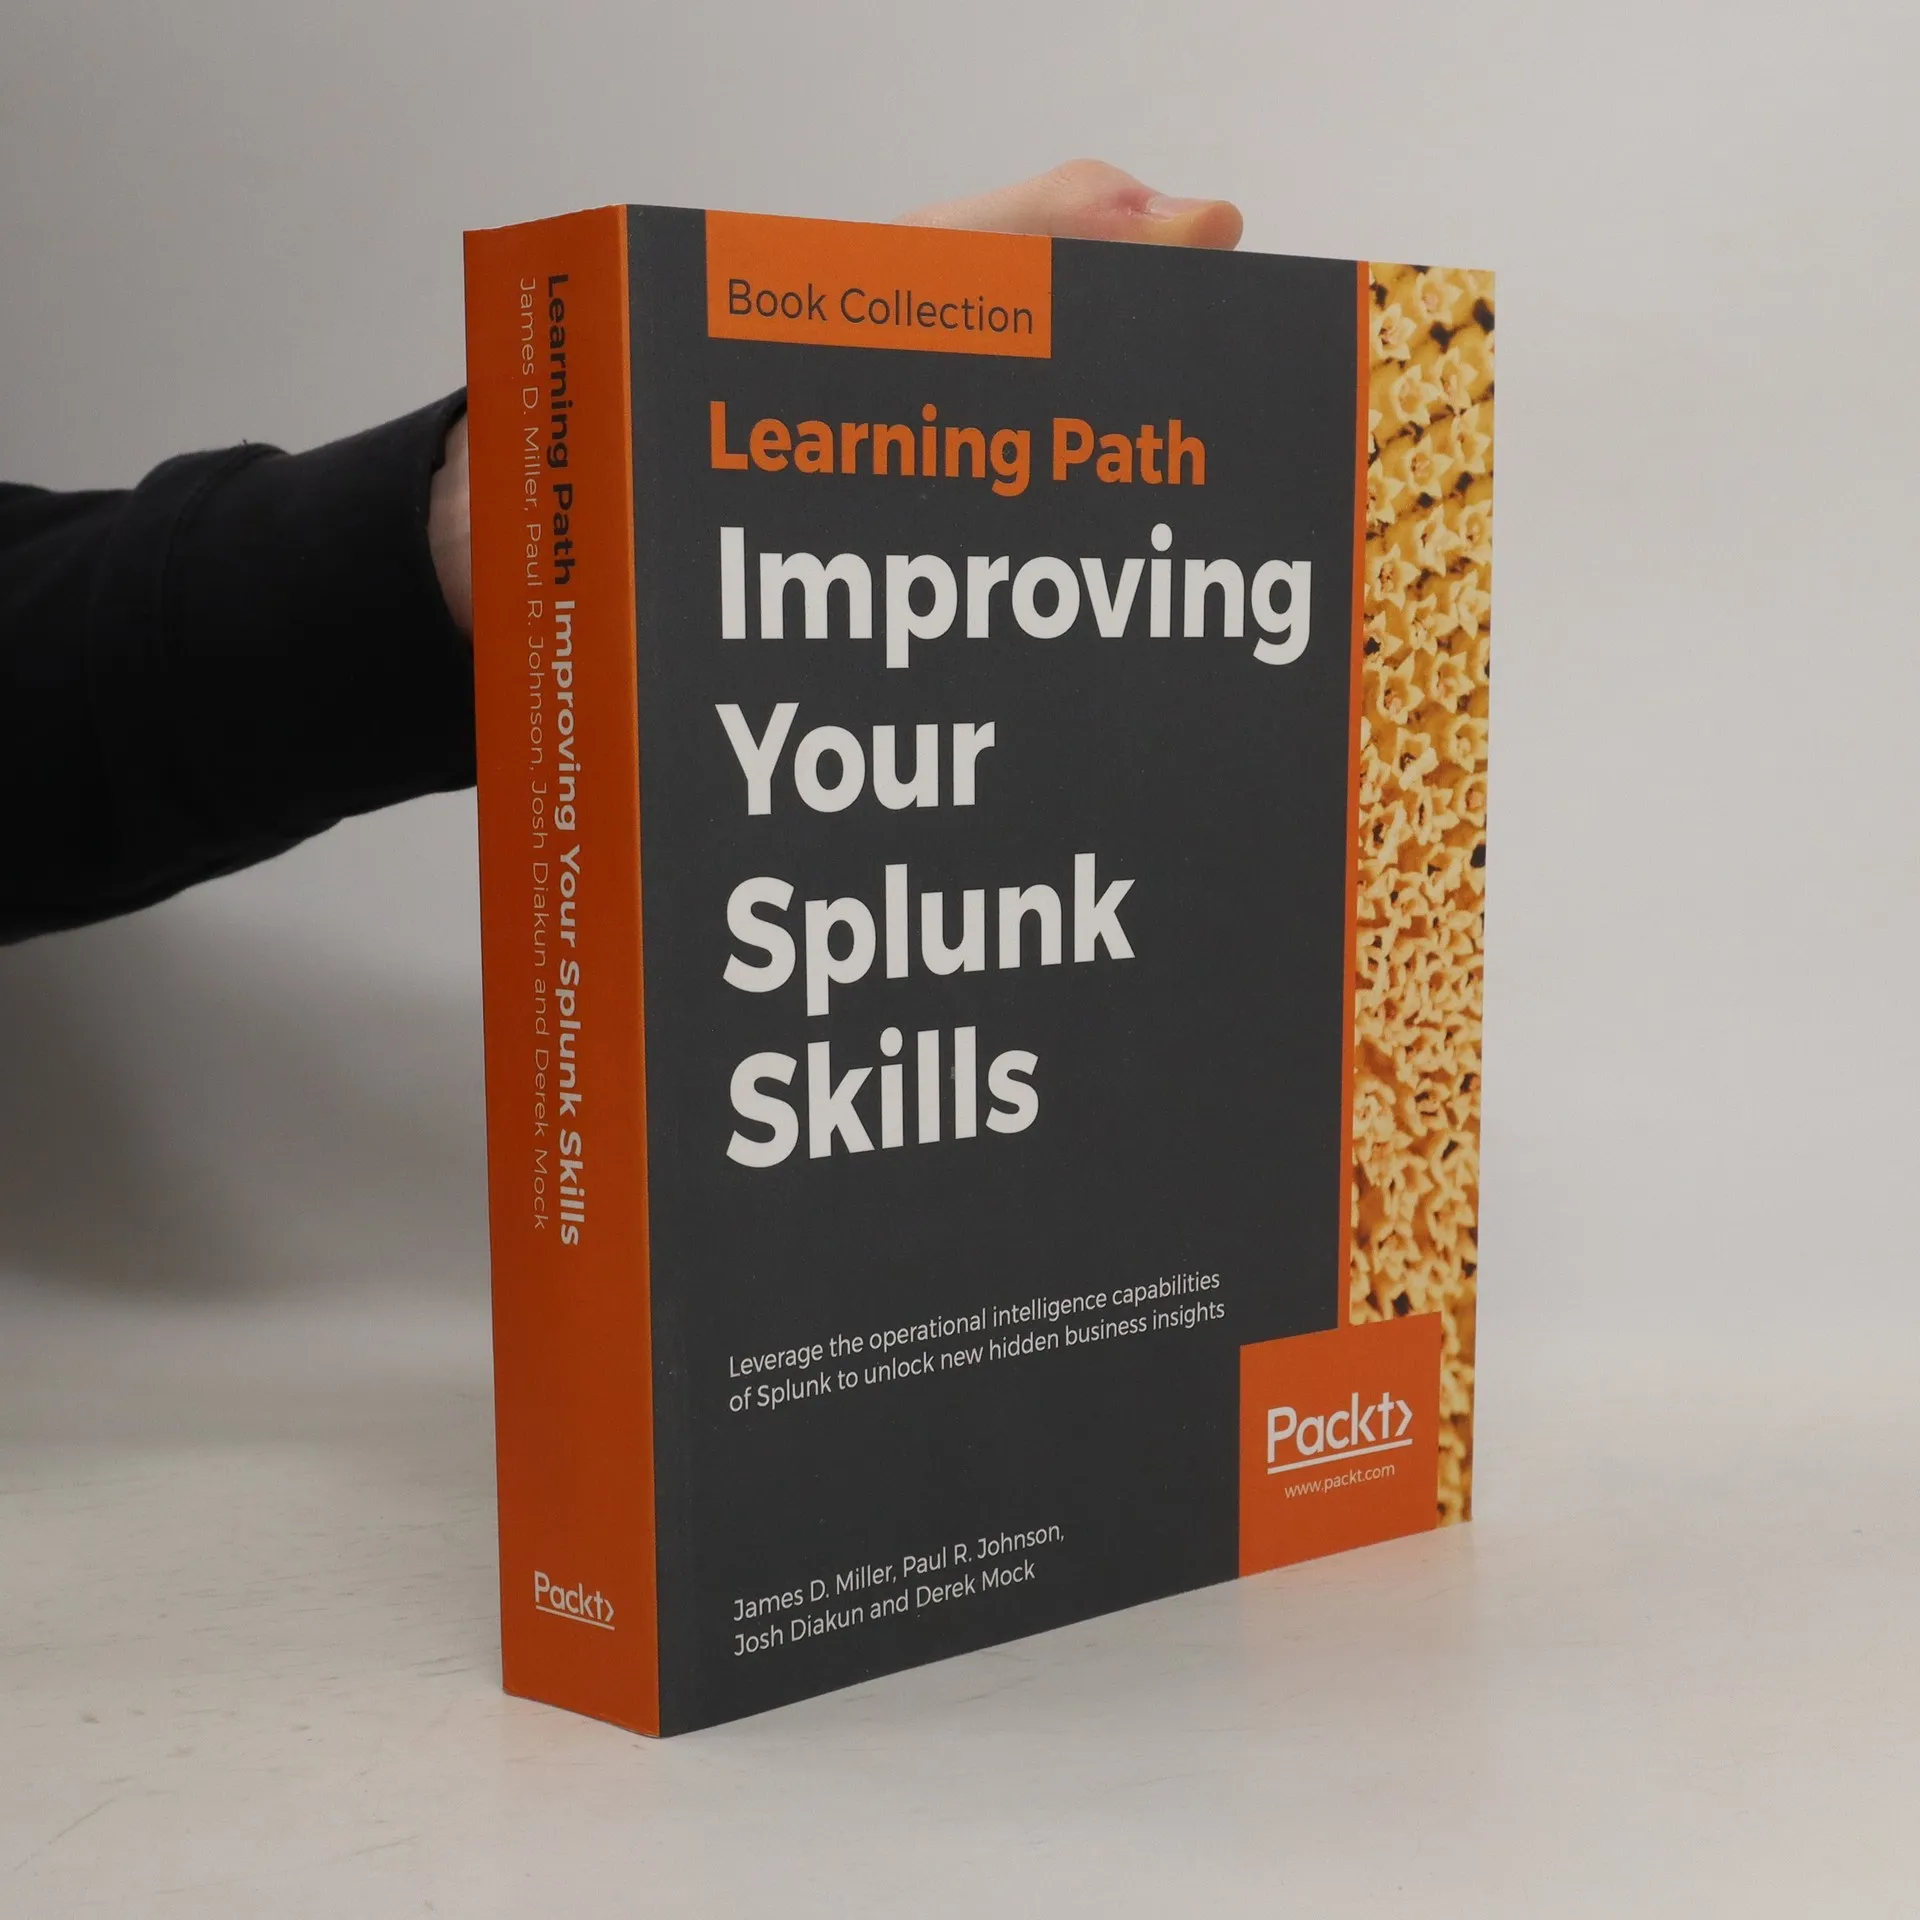


Więcej o książce
Transform machine-generated data into valuable business insights using Splunk. This Learning Path enables you to implement new services for efficiently processing big data. It begins with an introduction to the features and improvements of Splunk 7, teaching you to use wildcards and modify searches for enhanced performance. You'll learn to enhance applications through XML dashboards, configuration, and extension of Splunk, with step-by-step demonstrations for building operational intelligence applications. As you progress, you'll explore data models and pivots to expand your intelligence capabilities. By the end, you'll possess the skills to implement various Splunk services in your projects. Key learning outcomes include mastering Splunk Cloud and the Machine Learning Toolkit, creating efficient searches, and utilizing Splunk tables, charts, and graph enhancements. You'll also learn to work with data models and pivots, apply machine learning algorithms for forecasting and anomaly detection, and integrate advanced JavaScript charts while leveraging Splunk's API. This Learning Path is designed for data analysts, business analysts, and IT administrators looking to utilize Splunk as an operational intelligence tool. Existing users aiming to upgrade to Splunk 7.x will also benefit, especially with some prior knowledge of Splunk services.
Zakup książki
Improving Your Splunk Skills, Derek Mock, Josh Diakun, James D. Miller, Paul R. Johnson
- Język

- Rok wydania
- 2019
- Oprawa
- (miękka)
Metody płatności
Nikt jeszcze nie ocenił.
- Tytuł
- Improving Your Splunk Skills
- Język
- angielski
- Autorzy
- Derek Mock, Josh Diakun, James D. Miller, Paul R. Johnson
- Wydawca
- Packt Publishing
- Rok wydania
- 2019
- Oprawa
- miękka
- Liczba stron
- 680
- ISBN10
- 1838981748
- ISBN13
- 9781838981747
- Seria
- Tagi
- Opis
- Transform machine-generated data into valuable business insights using Splunk. This Learning Path enables you to implement new services for efficiently processing big data. It begins with an introduction to the features and improvements of Splunk 7, teaching you to use wildcards and modify searches for enhanced performance. You'll learn to enhance applications through XML dashboards, configuration, and extension of Splunk, with step-by-step demonstrations for building operational intelligence applications. As you progress, you'll explore data models and pivots to expand your intelligence capabilities. By the end, you'll possess the skills to implement various Splunk services in your projects. Key learning outcomes include mastering Splunk Cloud and the Machine Learning Toolkit, creating efficient searches, and utilizing Splunk tables, charts, and graph enhancements. You'll also learn to work with data models and pivots, apply machine learning algorithms for forecasting and anomaly detection, and integrate advanced JavaScript charts while leveraging Splunk's API. This Learning Path is designed for data analysts, business analysts, and IT administrators looking to utilize Splunk as an operational intelligence tool. Existing users aiming to upgrade to Splunk 7.x will also benefit, especially with some prior knowledge of Splunk services.