

Więcej o książce
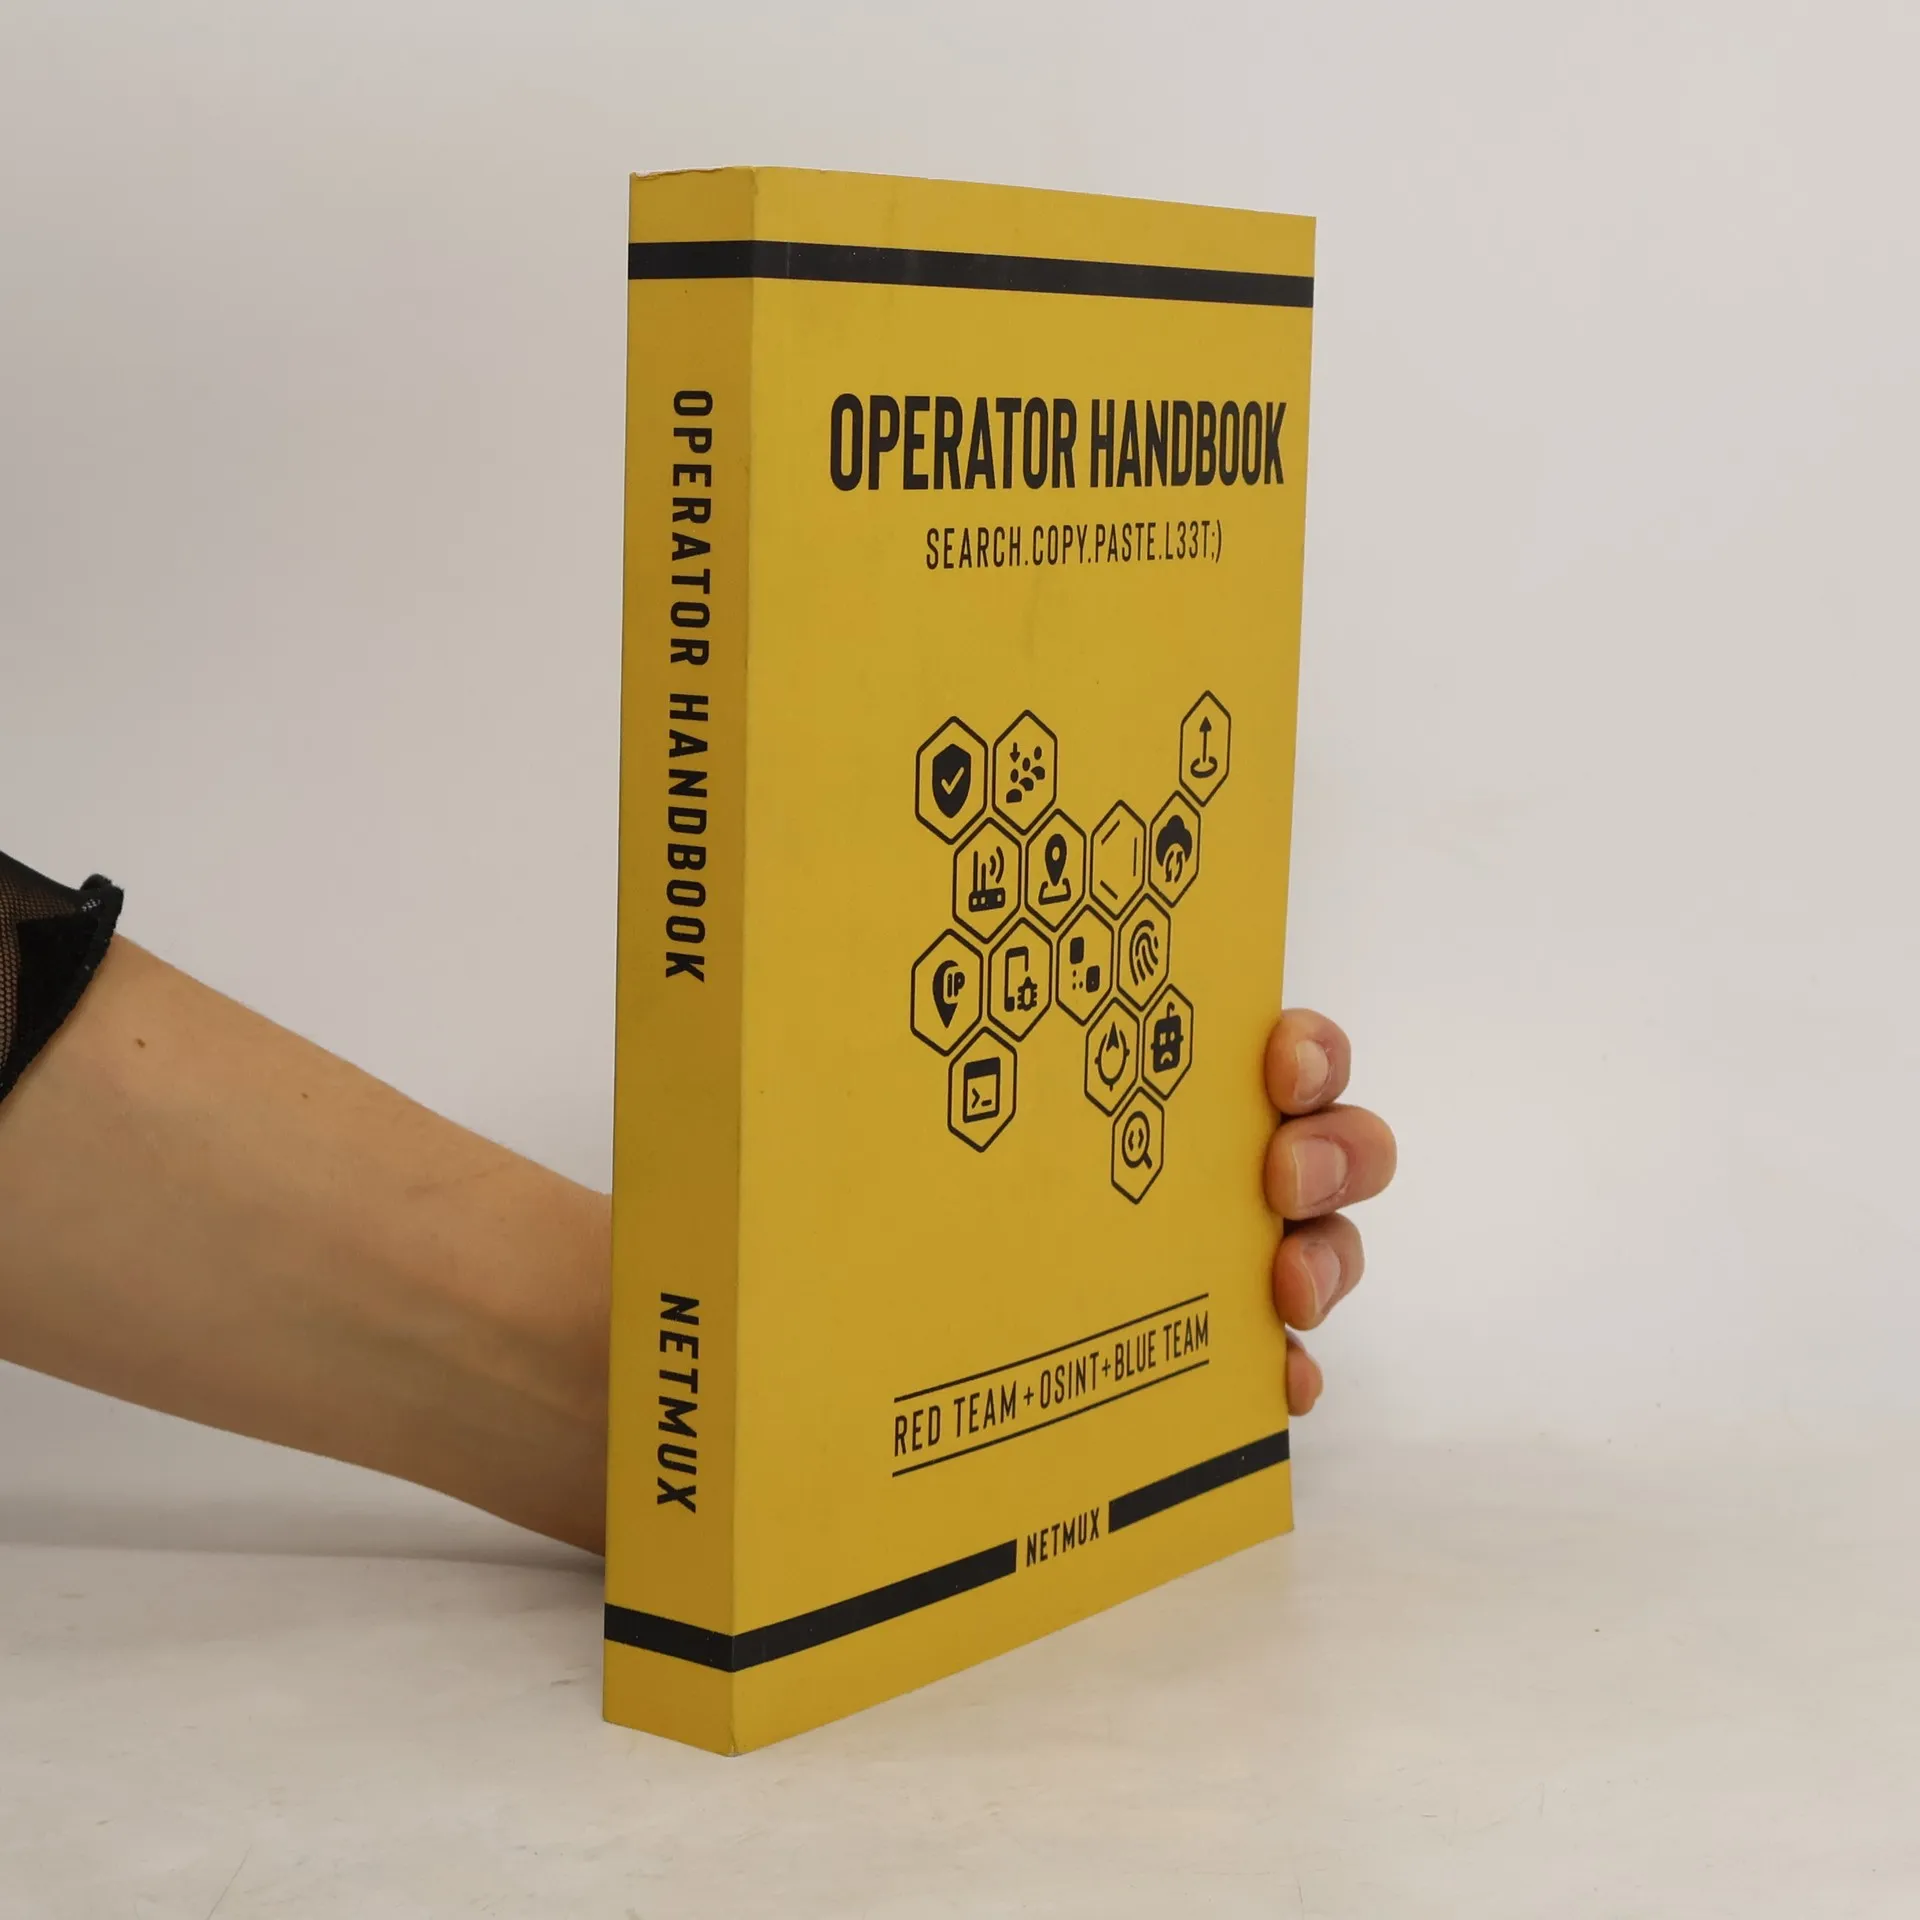
The Operator Handbook merges three disciplines—Red Team, OSINT, and Blue Team—into a comprehensive reference guide featuring over 100 cheat sheet references for commonly used tools and techniques. It caters to both seasoned cybersecurity veterans and newcomers, aiming to eliminate the artificial barriers that confine knowledge within specific teams. In today’s complex digital landscape, a well-rounded understanding across all areas is essential. The concept of "Operator" culture emphasizes that all cybersecurity practitioners are Operators, with Blue Team members learning Red Team tactics, Red Team fostering collaboration with Blue Team, and OSINT uncovering evidence of wrongdoing from diverse data sources. To enhance accessibility, references are organized alphabetically, facilitating quicker lookups and promoting a unified approach. Each topic is examined from both "How to exploit X" and "How to defend X" perspectives. Coverage includes Cloud Services, Operating Systems, Mobile, OSINT, Ports, Forensics, Malware Resources, and various tools (e.g., Defender tools, Attacker tools, and supporting tools like Vim and iptables). This handbook serves as a singular resource for the most prevalent tools and techniques an Operator may encounter in their work.
Zakup książki
Operator Handbook, Joshua Picolet
- Język

- Rok wydania
- 2020
- Oprawa
- (miękka)
Metody płatności
Brakuje nam tutaj Twojej recenzji.
- Tytuł
- Operator Handbook
- Podtytuł
- Red Team + OSINT + Blue Team Reference
- Język
- angielski
- Autorzy
- Joshua Picolet
- Wydawca
- Independently published
- Rok wydania
- 2020
- Oprawa
- miękka
- Liczba stron
- 335
- ISBN13
- 9798605493952
- Seria
- Ocena
- 4,35 z 5
- Opis
- The Operator Handbook merges three disciplines—Red Team, OSINT, and Blue Team—into a comprehensive reference guide featuring over 100 cheat sheet references for commonly used tools and techniques. It caters to both seasoned cybersecurity veterans and newcomers, aiming to eliminate the artificial barriers that confine knowledge within specific teams. In today’s complex digital landscape, a well-rounded understanding across all areas is essential. The concept of "Operator" culture emphasizes that all cybersecurity practitioners are Operators, with Blue Team members learning Red Team tactics, Red Team fostering collaboration with Blue Team, and OSINT uncovering evidence of wrongdoing from diverse data sources. To enhance accessibility, references are organized alphabetically, facilitating quicker lookups and promoting a unified approach. Each topic is examined from both "How to exploit X" and "How to defend X" perspectives. Coverage includes Cloud Services, Operating Systems, Mobile, OSINT, Ports, Forensics, Malware Resources, and various tools (e.g., Defender tools, Attacker tools, and supporting tools like Vim and iptables). This handbook serves as a singular resource for the most prevalent tools and techniques an Operator may encounter in their work.