

Więcej o książce
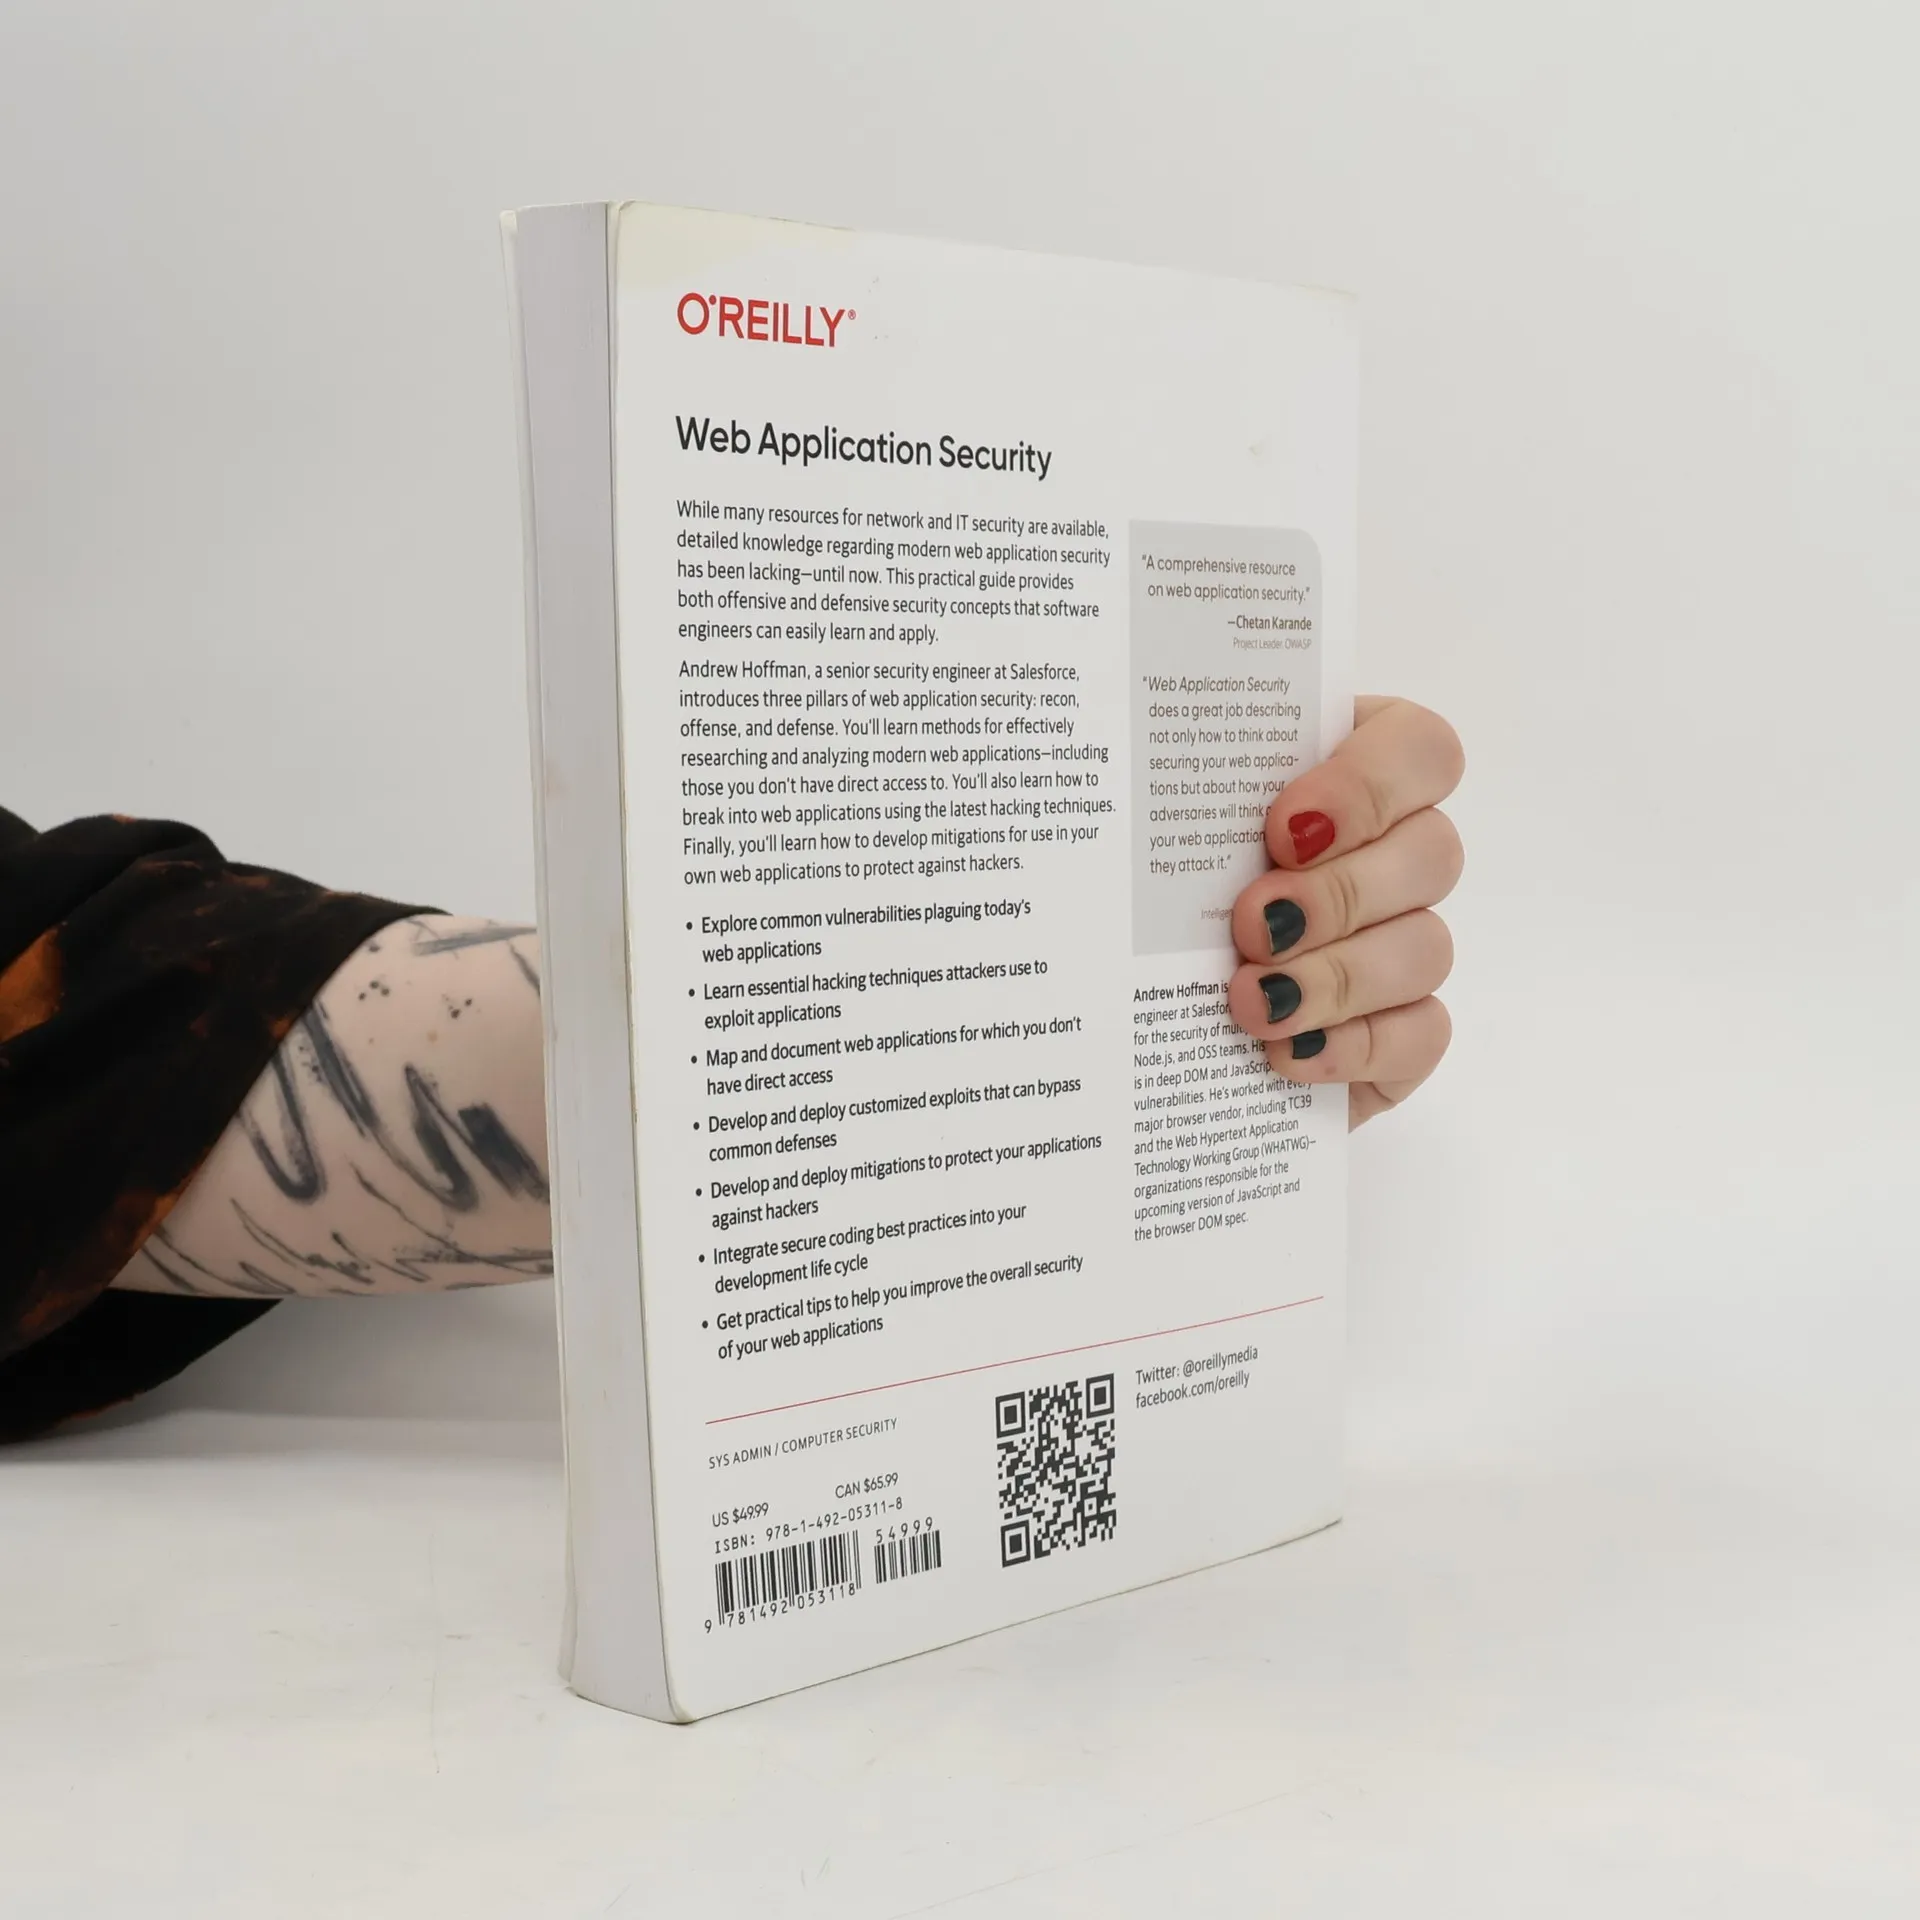
While many resources for network and IT security are available, detailed knowledge regarding modern web application security has been lacking--until now. This practical guide provides both offensive and defensive security concepts that software engineers can easily learn and apply. Andrew Hoffman, a senior security engineer at Salesforce, introduces three pillars of web application security: recon, offense, and defense. You'll learn methods for effectively researching and analyzing modern web applications--including those you don't have direct access to. You'll also learn how to break into web applications using the latest hacking techniques. Finally, you'll learn how to develop mitigations for use in your own web applications to protect against hackers. Explore common vulnerabilities plaguing today's web applications Learn essential hacking techniques attackers use to exploit applications Map and document web applications for which you don't have direct access Develop and deploy customized exploits that can bypass common defenses Develop and deploy mitigations to protect your applications against hackers Integrate secure coding best practices into your development lifecycle Get practical tips to help you improve the overall security of your web applications
Zakup książki
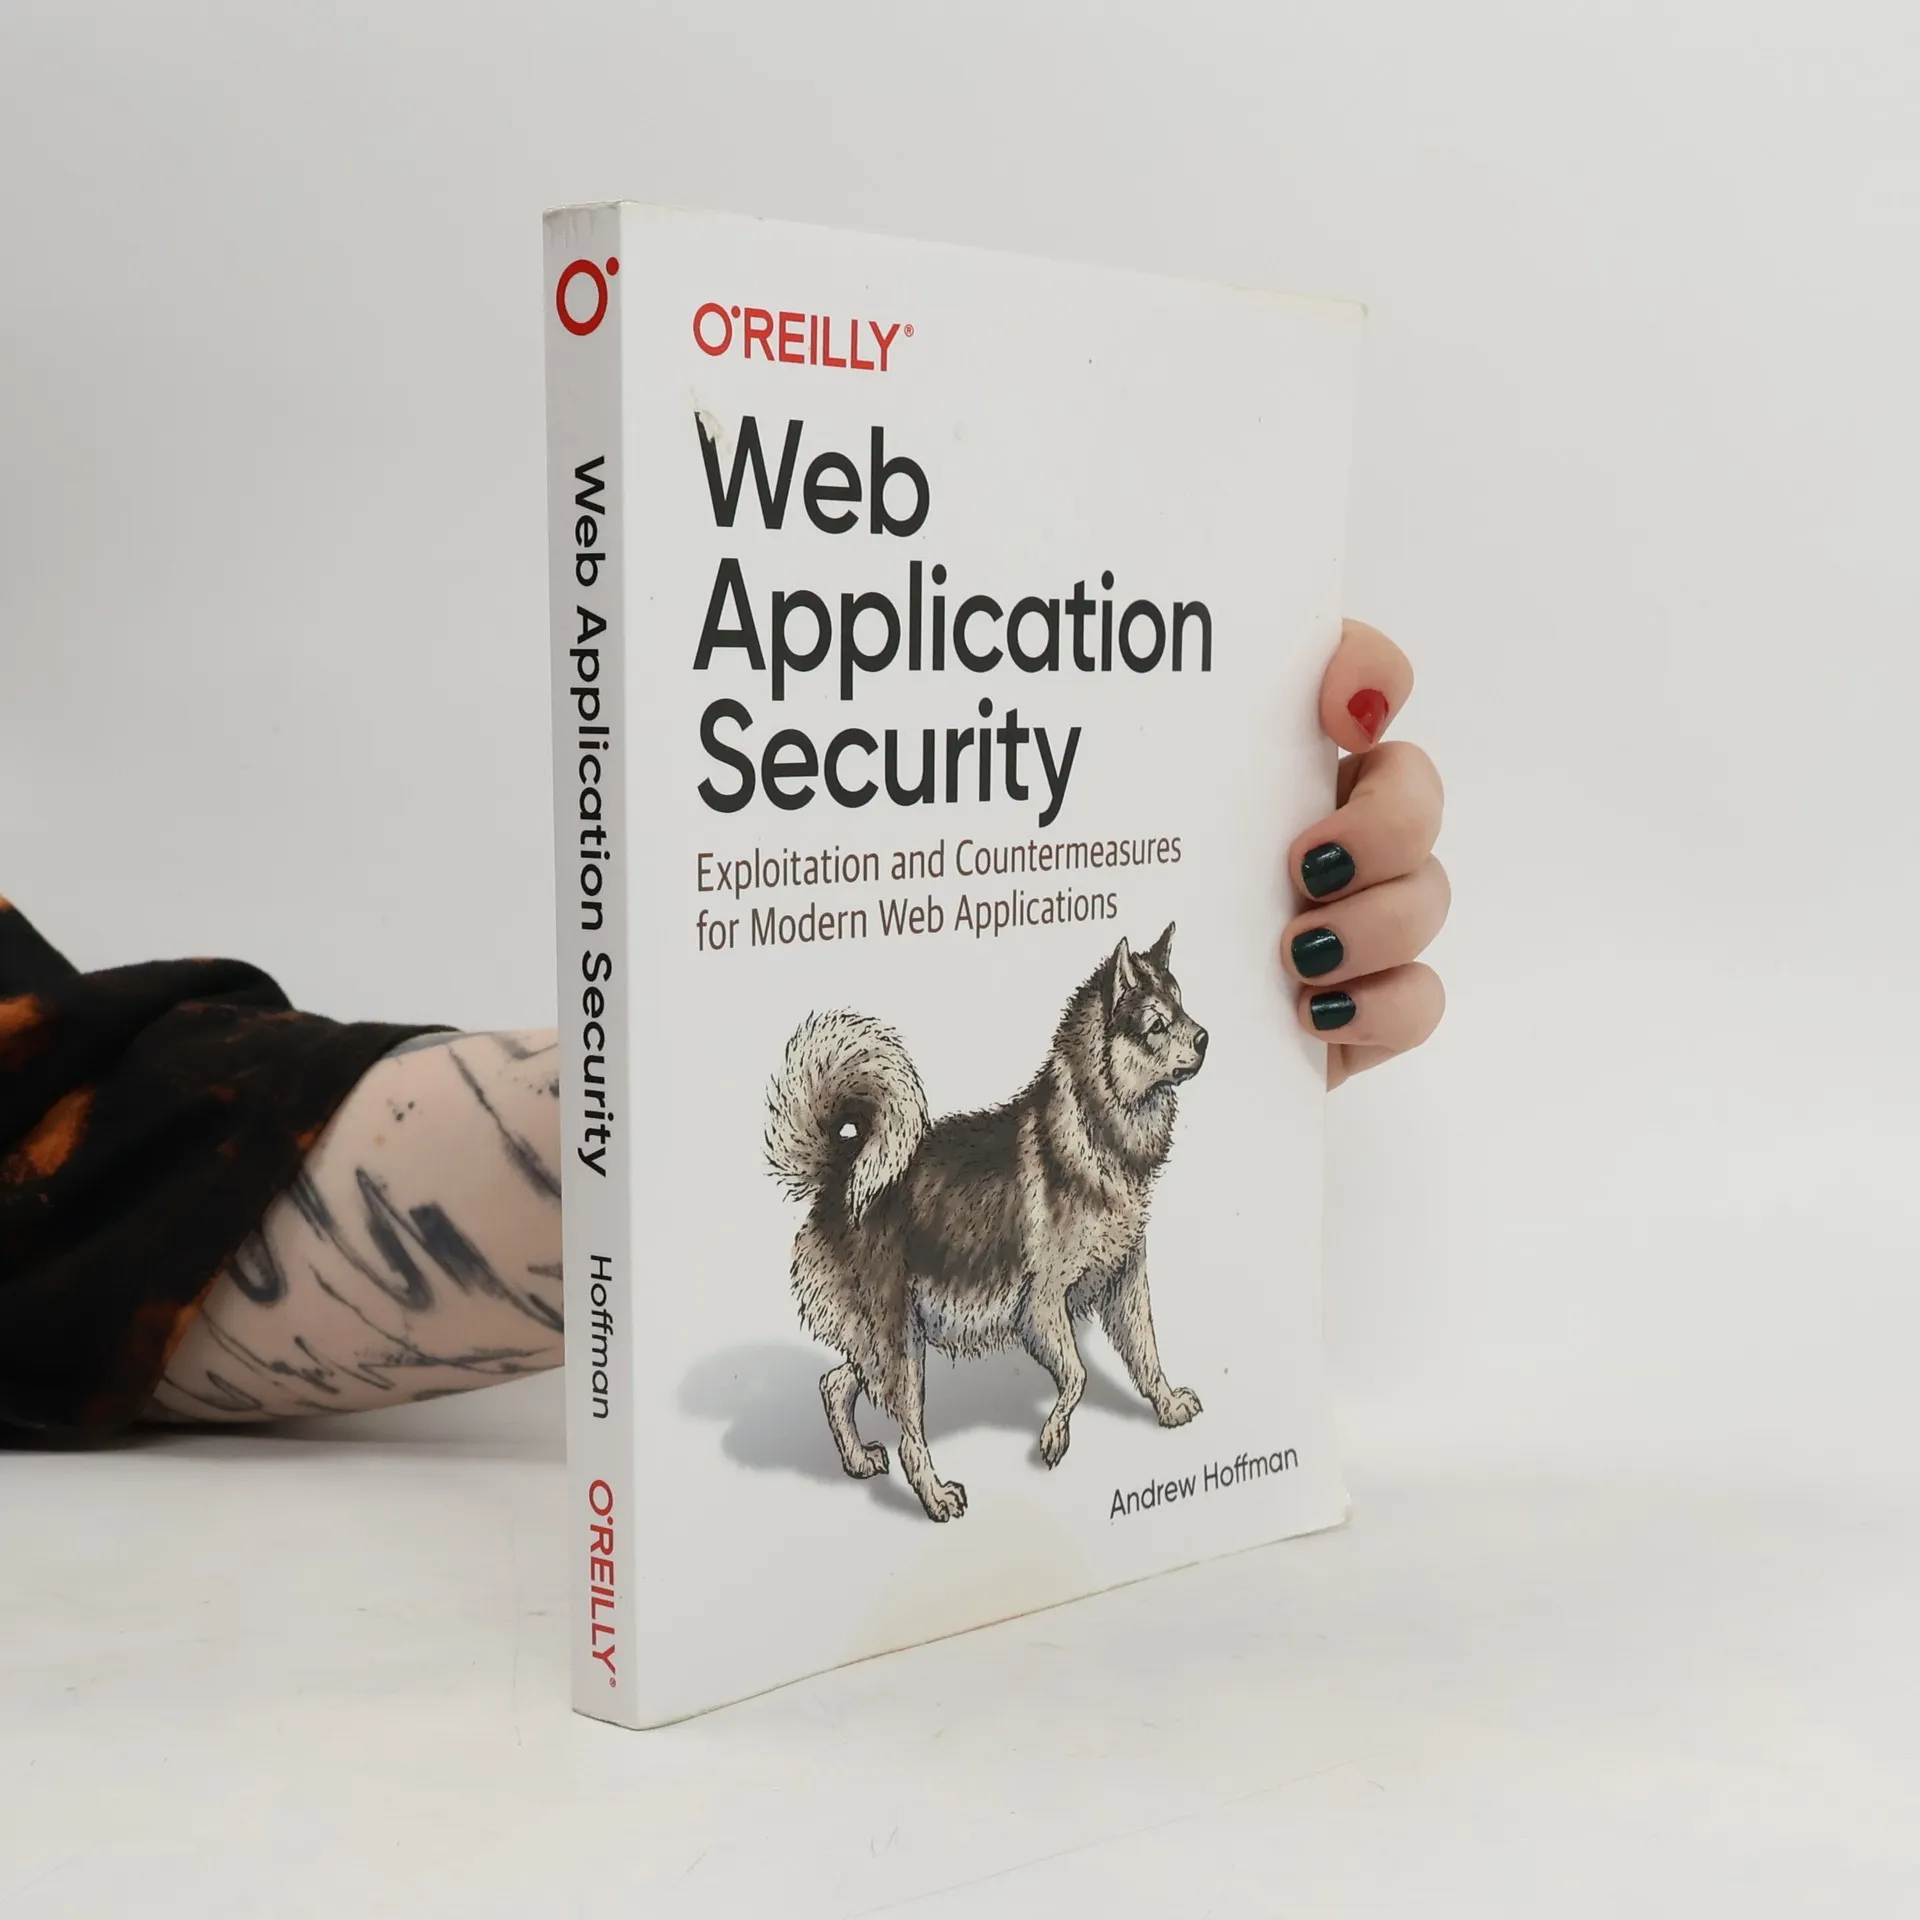
Web Application Security, Andrew Hoffman
- Język

- Rok wydania
- 2020
- Oprawa
- (miękka)
Metody płatności
Nikt jeszcze nie ocenił.
- Tytuł
- Web Application Security
- Podtytuł
- Exploitation and Countermeasures for Modern Web Applications
- Język
- angielski
- Autorzy
- Andrew Hoffman
- Wydawca
- O'Reilly Media
- Rok wydania
- 2020
- Oprawa
- miękka
- Liczba stron
- 298
- ISBN10
- 1492053112
- ISBN13
- 9781492053118
- Seria
- Opis
- While many resources for network and IT security are available, detailed knowledge regarding modern web application security has been lacking--until now. This practical guide provides both offensive and defensive security concepts that software engineers can easily learn and apply. Andrew Hoffman, a senior security engineer at Salesforce, introduces three pillars of web application security: recon, offense, and defense. You'll learn methods for effectively researching and analyzing modern web applications--including those you don't have direct access to. You'll also learn how to break into web applications using the latest hacking techniques. Finally, you'll learn how to develop mitigations for use in your own web applications to protect against hackers. Explore common vulnerabilities plaguing today's web applications Learn essential hacking techniques attackers use to exploit applications Map and document web applications for which you don't have direct access Develop and deploy customized exploits that can bypass common defenses Develop and deploy mitigations to protect your applications against hackers Integrate secure coding best practices into your development lifecycle Get practical tips to help you improve the overall security of your web applications