

Więcej o książce
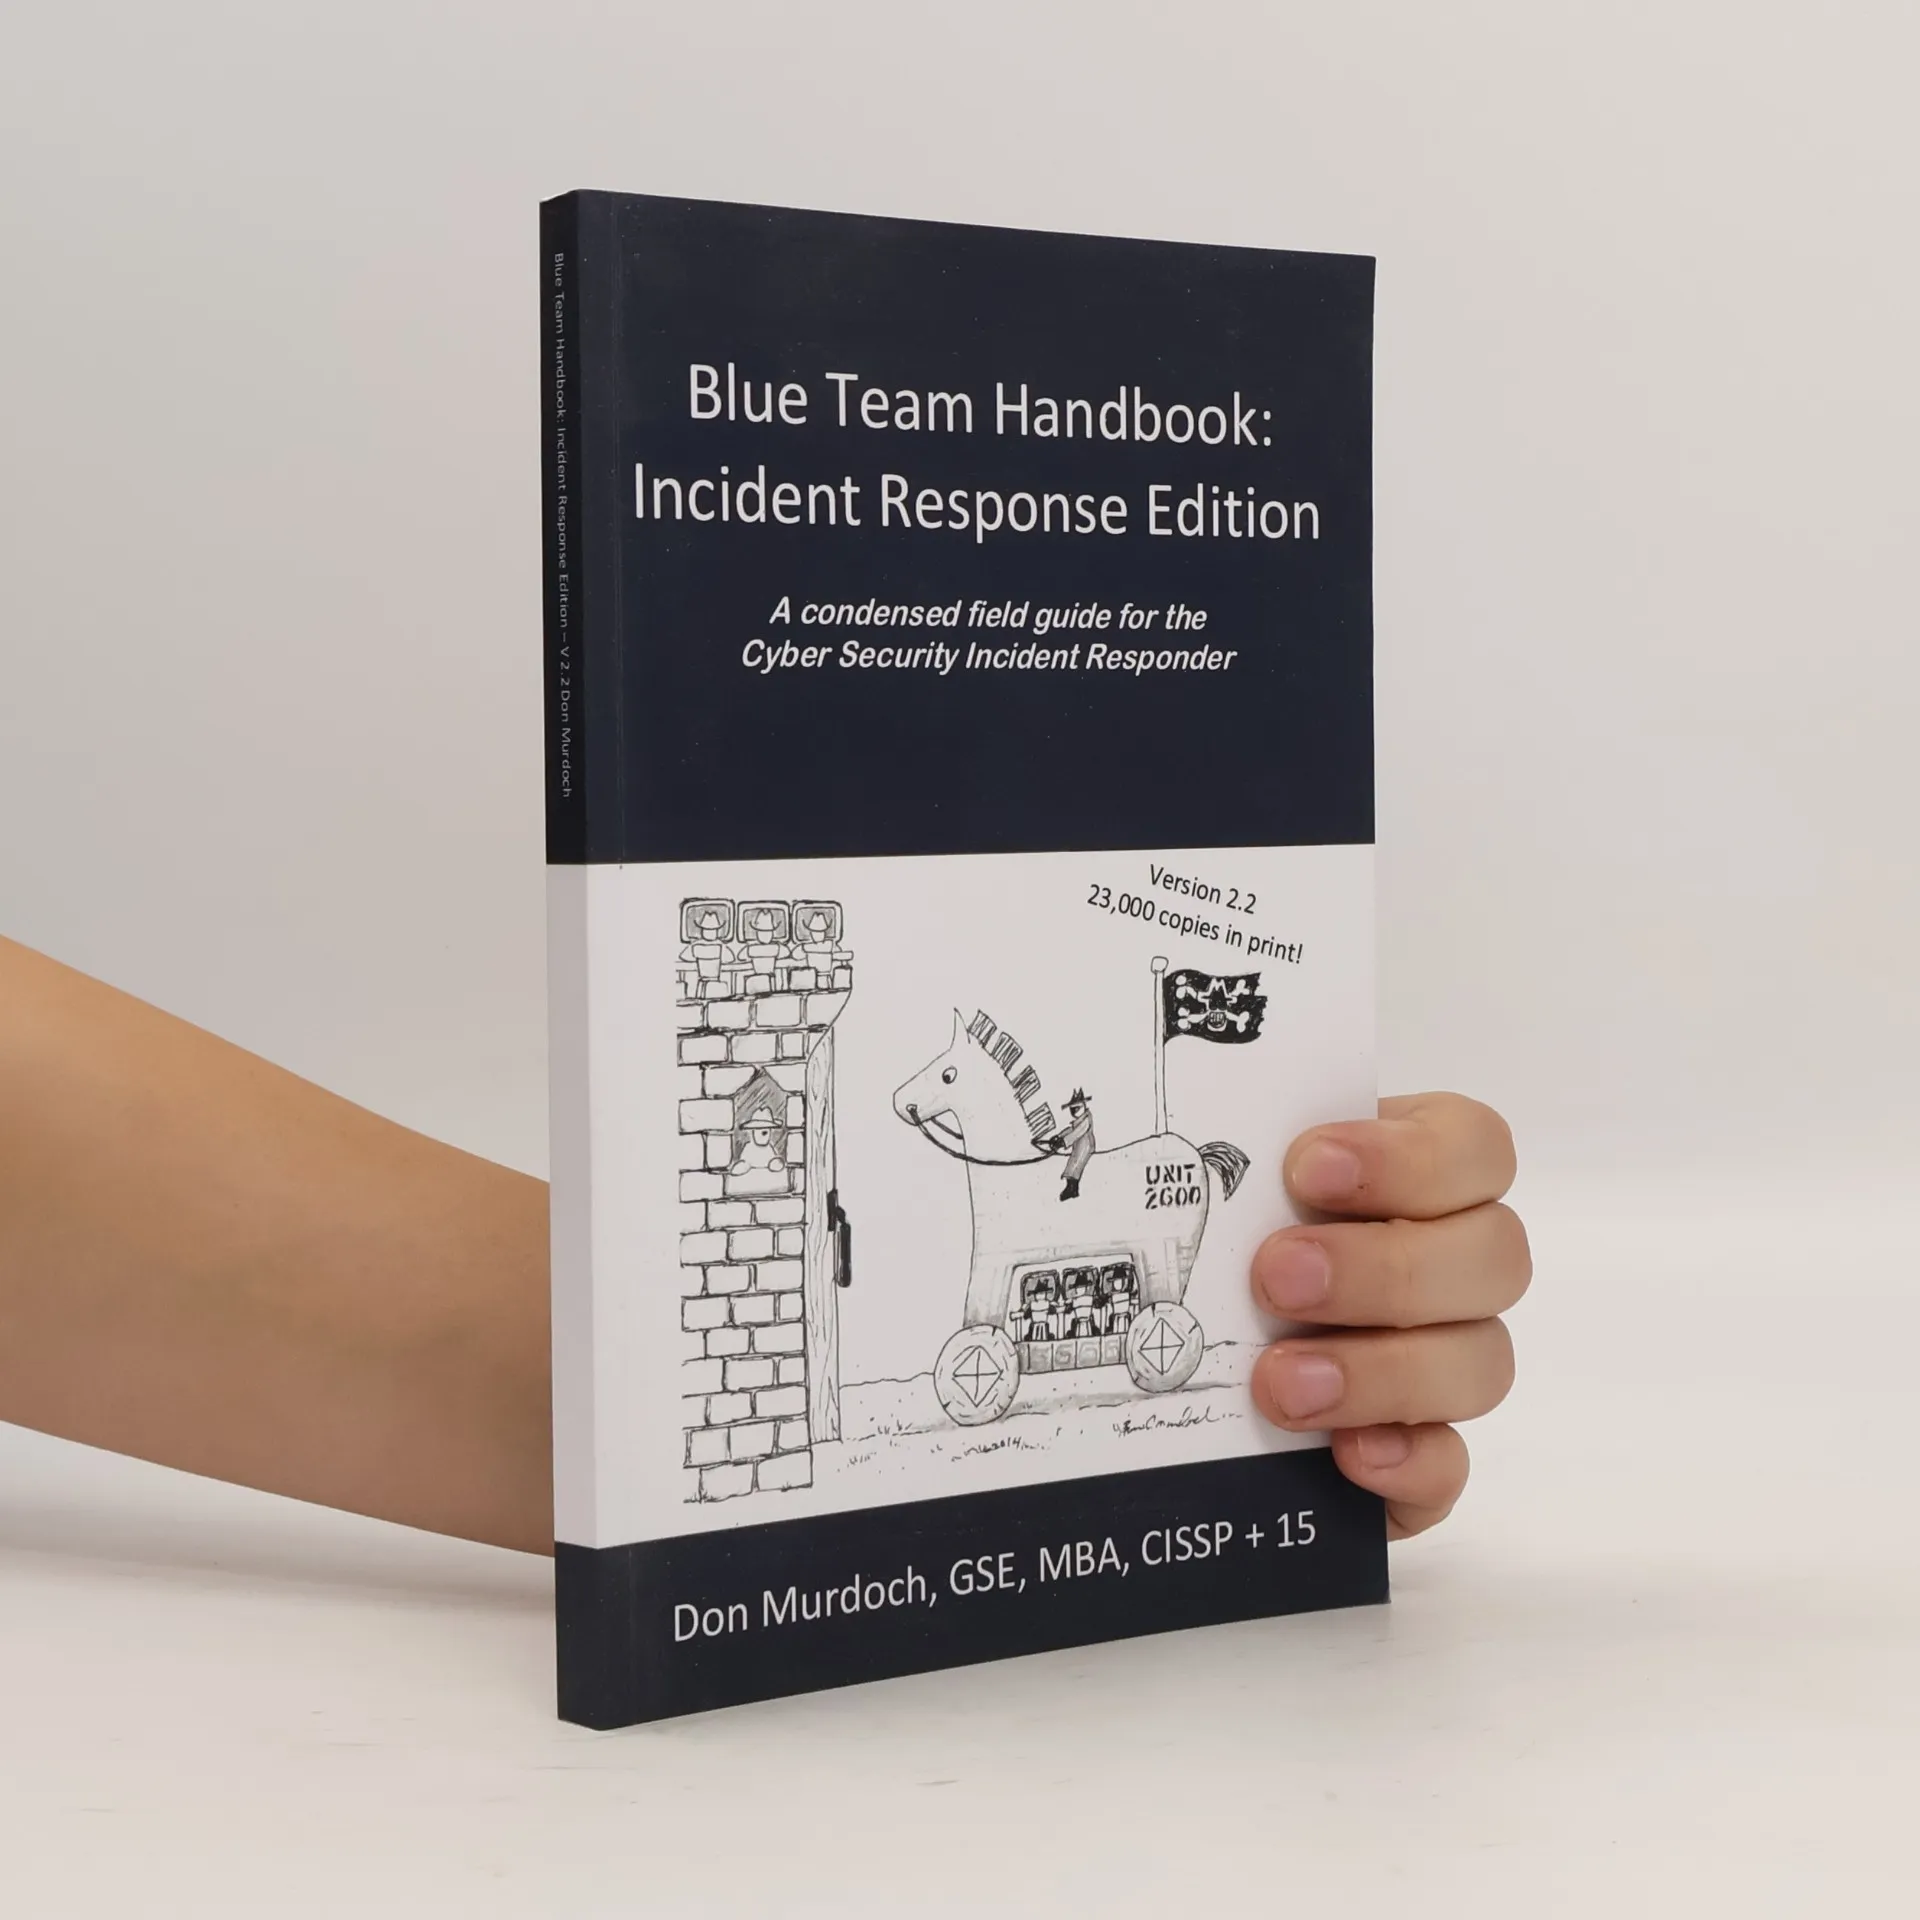
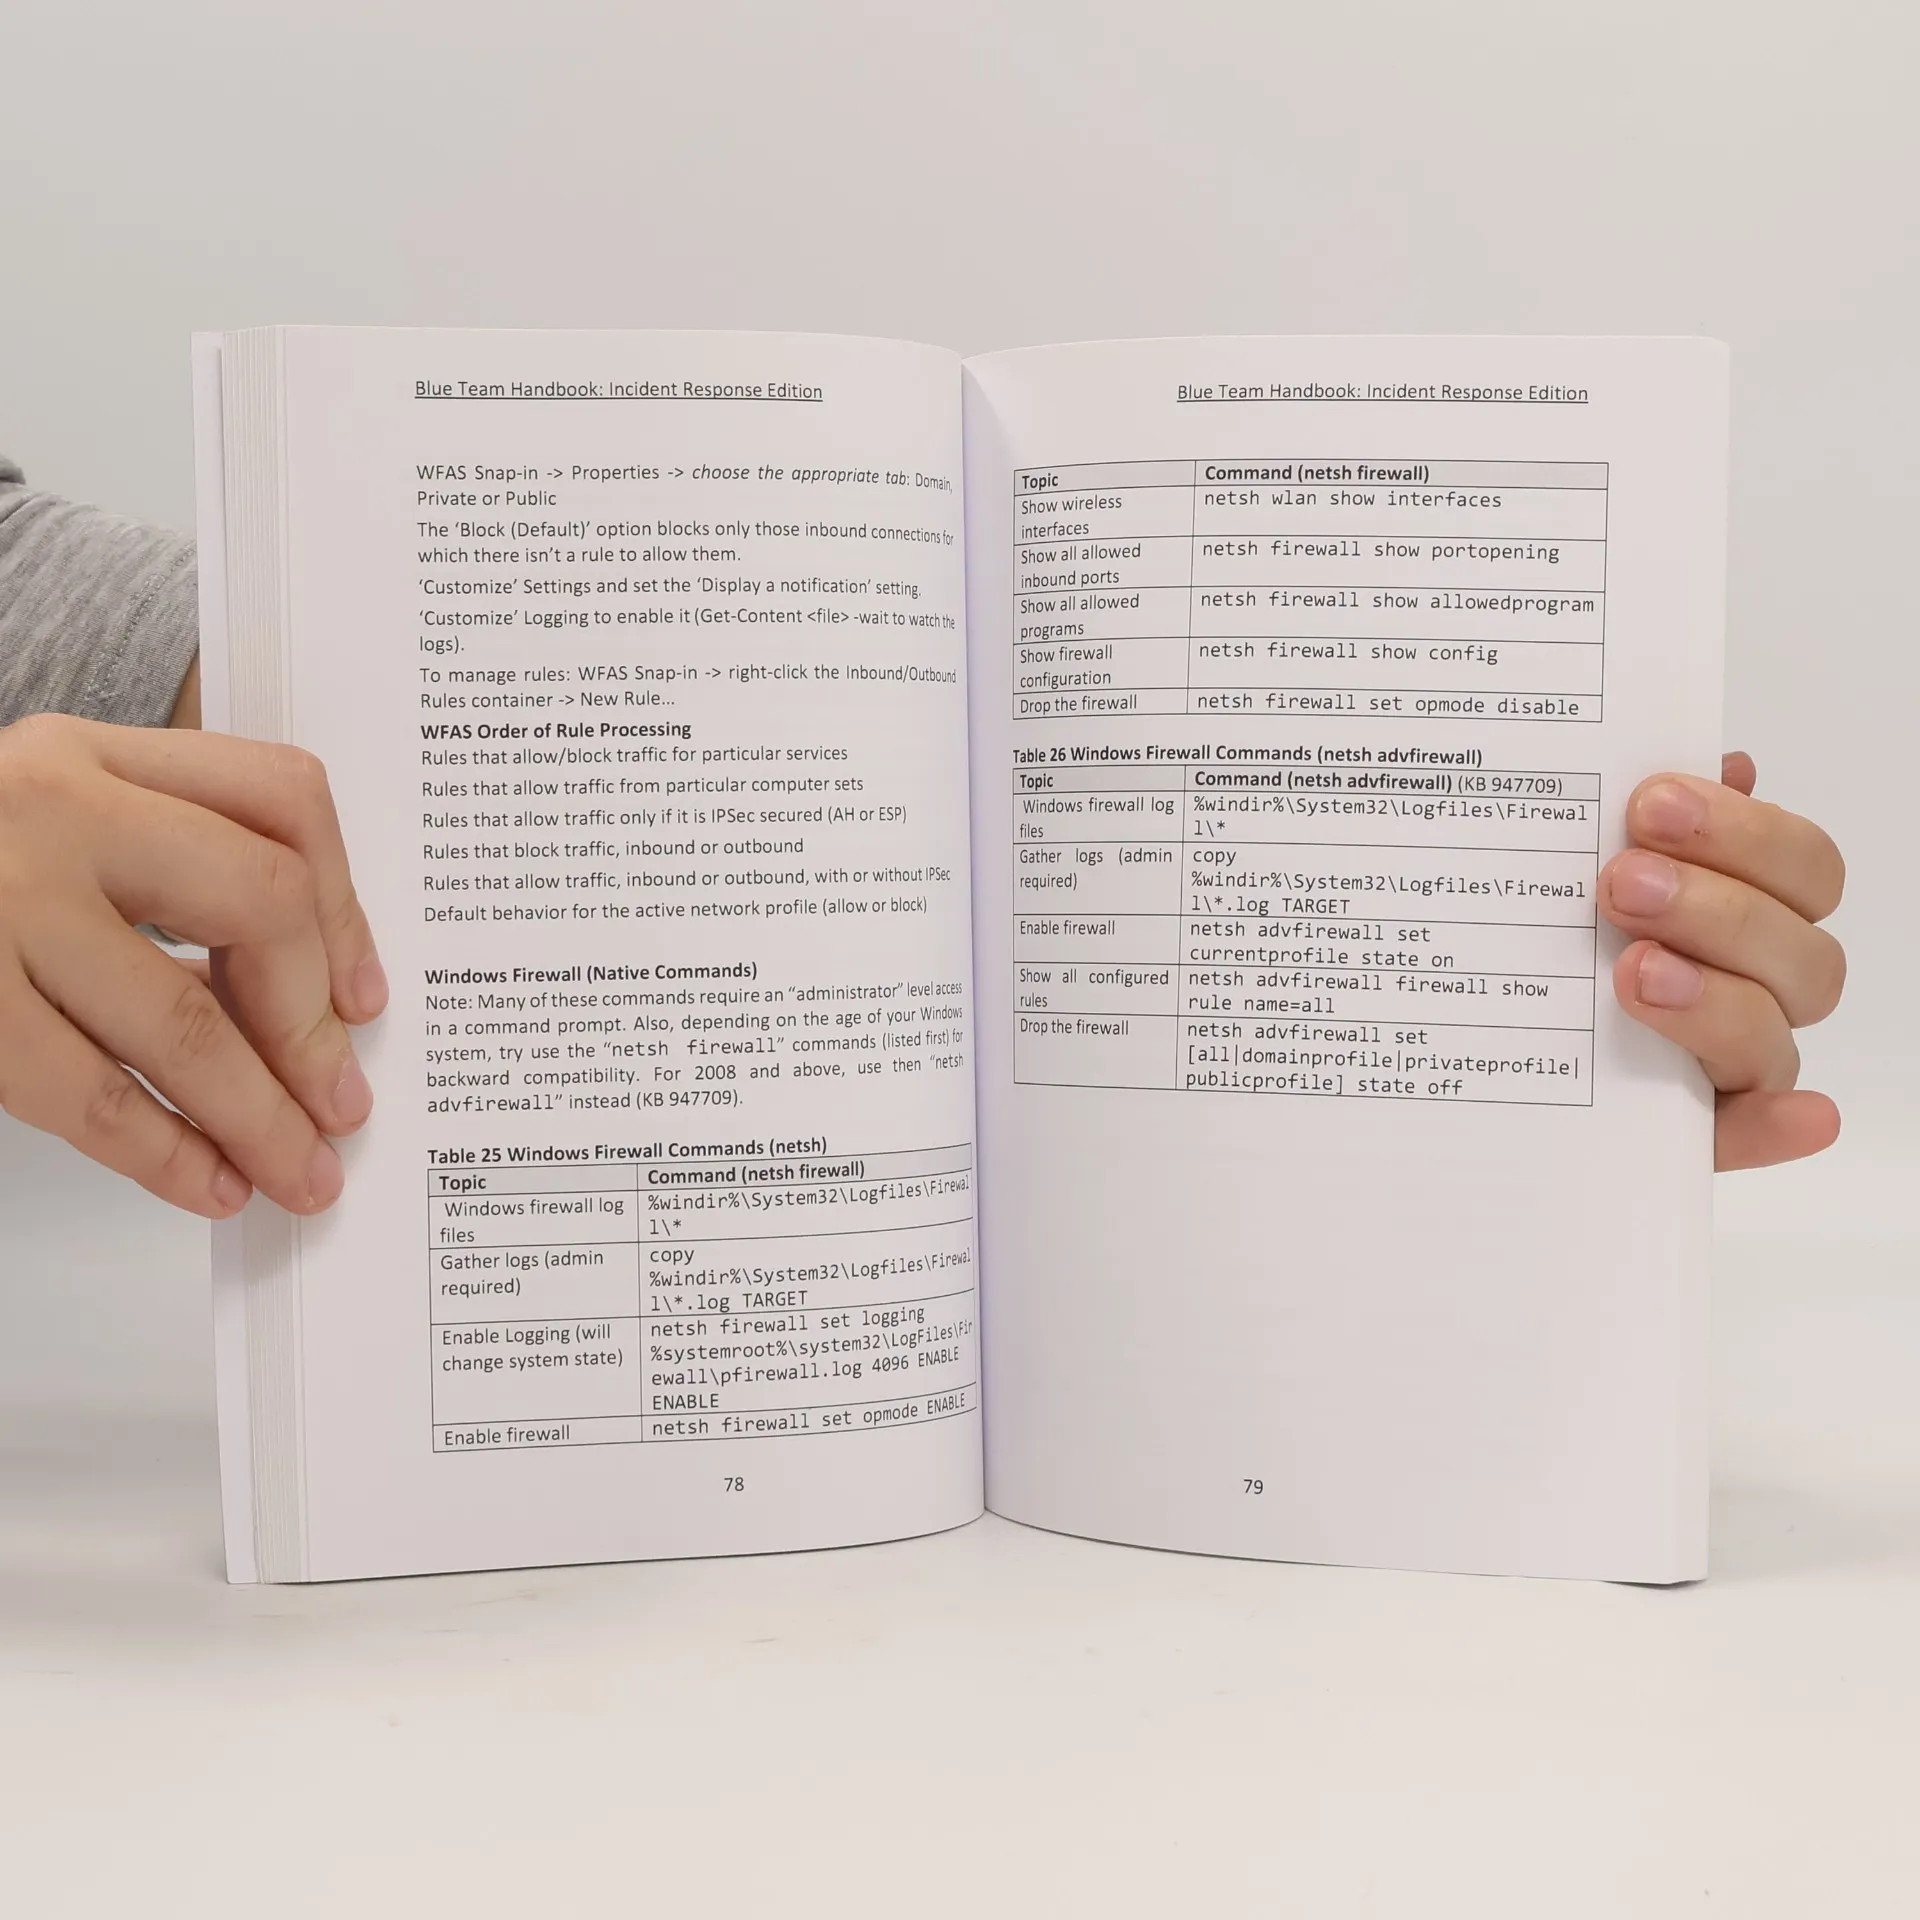
The Blue Team Handbook is a "zero fluff" reference guide for cyber security incident responders, security engineers, and InfoSec pros alike. The BTHb includes essential information in a condensed handbook format. Main topics include the incident response process, how attackers work, common tools for incident response, a methodology for network analysis, common indicators of compromise, Windows and Linux analysis processes, tcpdump usage examples, Snort IDS usage, packet headers, and numerous other quick reference topics. The book is designed specifically to share "real life experience," so it is peppered with practical techniques from the authors' extensive career in handling incidents. Whether you are writing up your cases notes, analyzing potentially suspicious traffic, or called in to look over a misbehaving server - this book should help you handle the case and teach you some new techniques along the way.
Zakup książki
Blue Team Handbook, D. W. Murdoch
- Język

- Rok wydania
- 2014
- Oprawa
- (miękka)
Metody płatności
Nikt jeszcze nie ocenił.
- Tytuł
- Blue Team Handbook
- Podtytuł
- Incident Response Edition: A Condensed Field Guide for the Cyber Security Incident Responder
- Język
- angielski
- Autorzy
- D. W. Murdoch
- Wydawca
- Createspace
- Rok wydania
- 2014
- Oprawa
- miękka
- Liczba stron
- 164
- ISBN10
- 1500734756
- ISBN13
- 9781500734756
- Seria
- Opis
- The Blue Team Handbook is a "zero fluff" reference guide for cyber security incident responders, security engineers, and InfoSec pros alike. The BTHb includes essential information in a condensed handbook format. Main topics include the incident response process, how attackers work, common tools for incident response, a methodology for network analysis, common indicators of compromise, Windows and Linux analysis processes, tcpdump usage examples, Snort IDS usage, packet headers, and numerous other quick reference topics. The book is designed specifically to share "real life experience," so it is peppered with practical techniques from the authors' extensive career in handling incidents. Whether you are writing up your cases notes, analyzing potentially suspicious traffic, or called in to look over a misbehaving server - this book should help you handle the case and teach you some new techniques along the way.