
Kupujesz dokładnie tę książkę,która jest na zdjęciu.
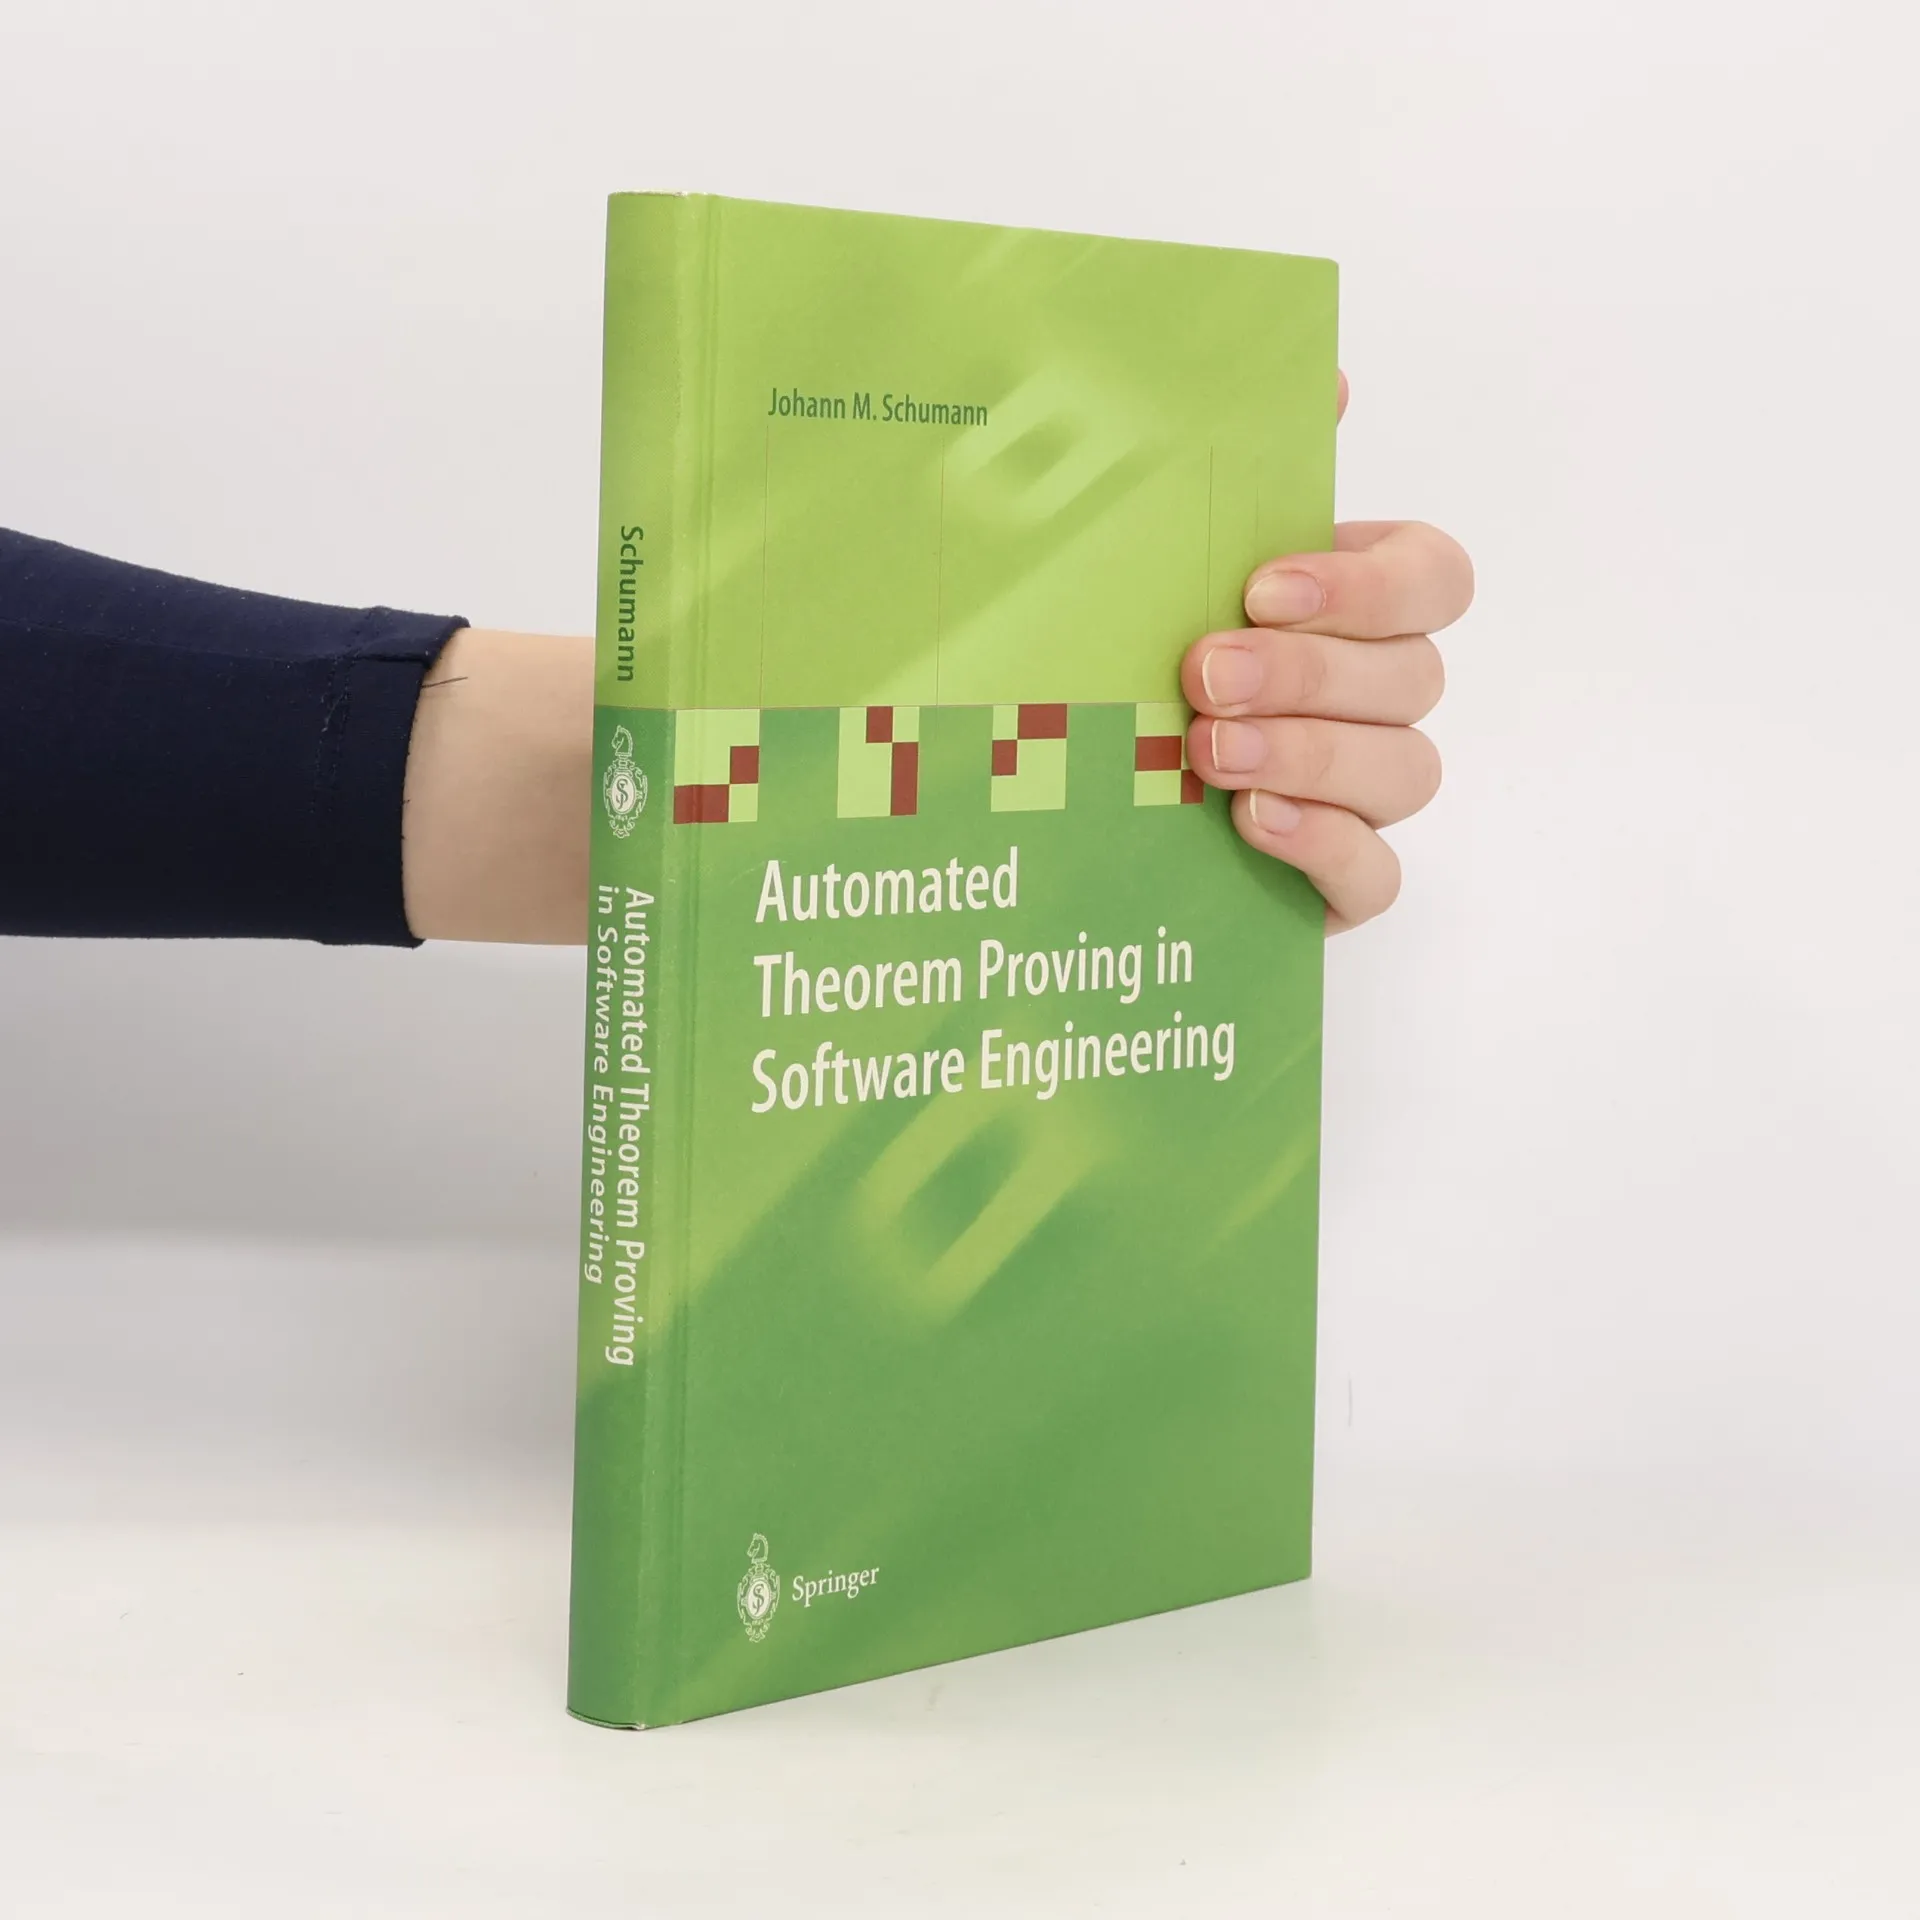
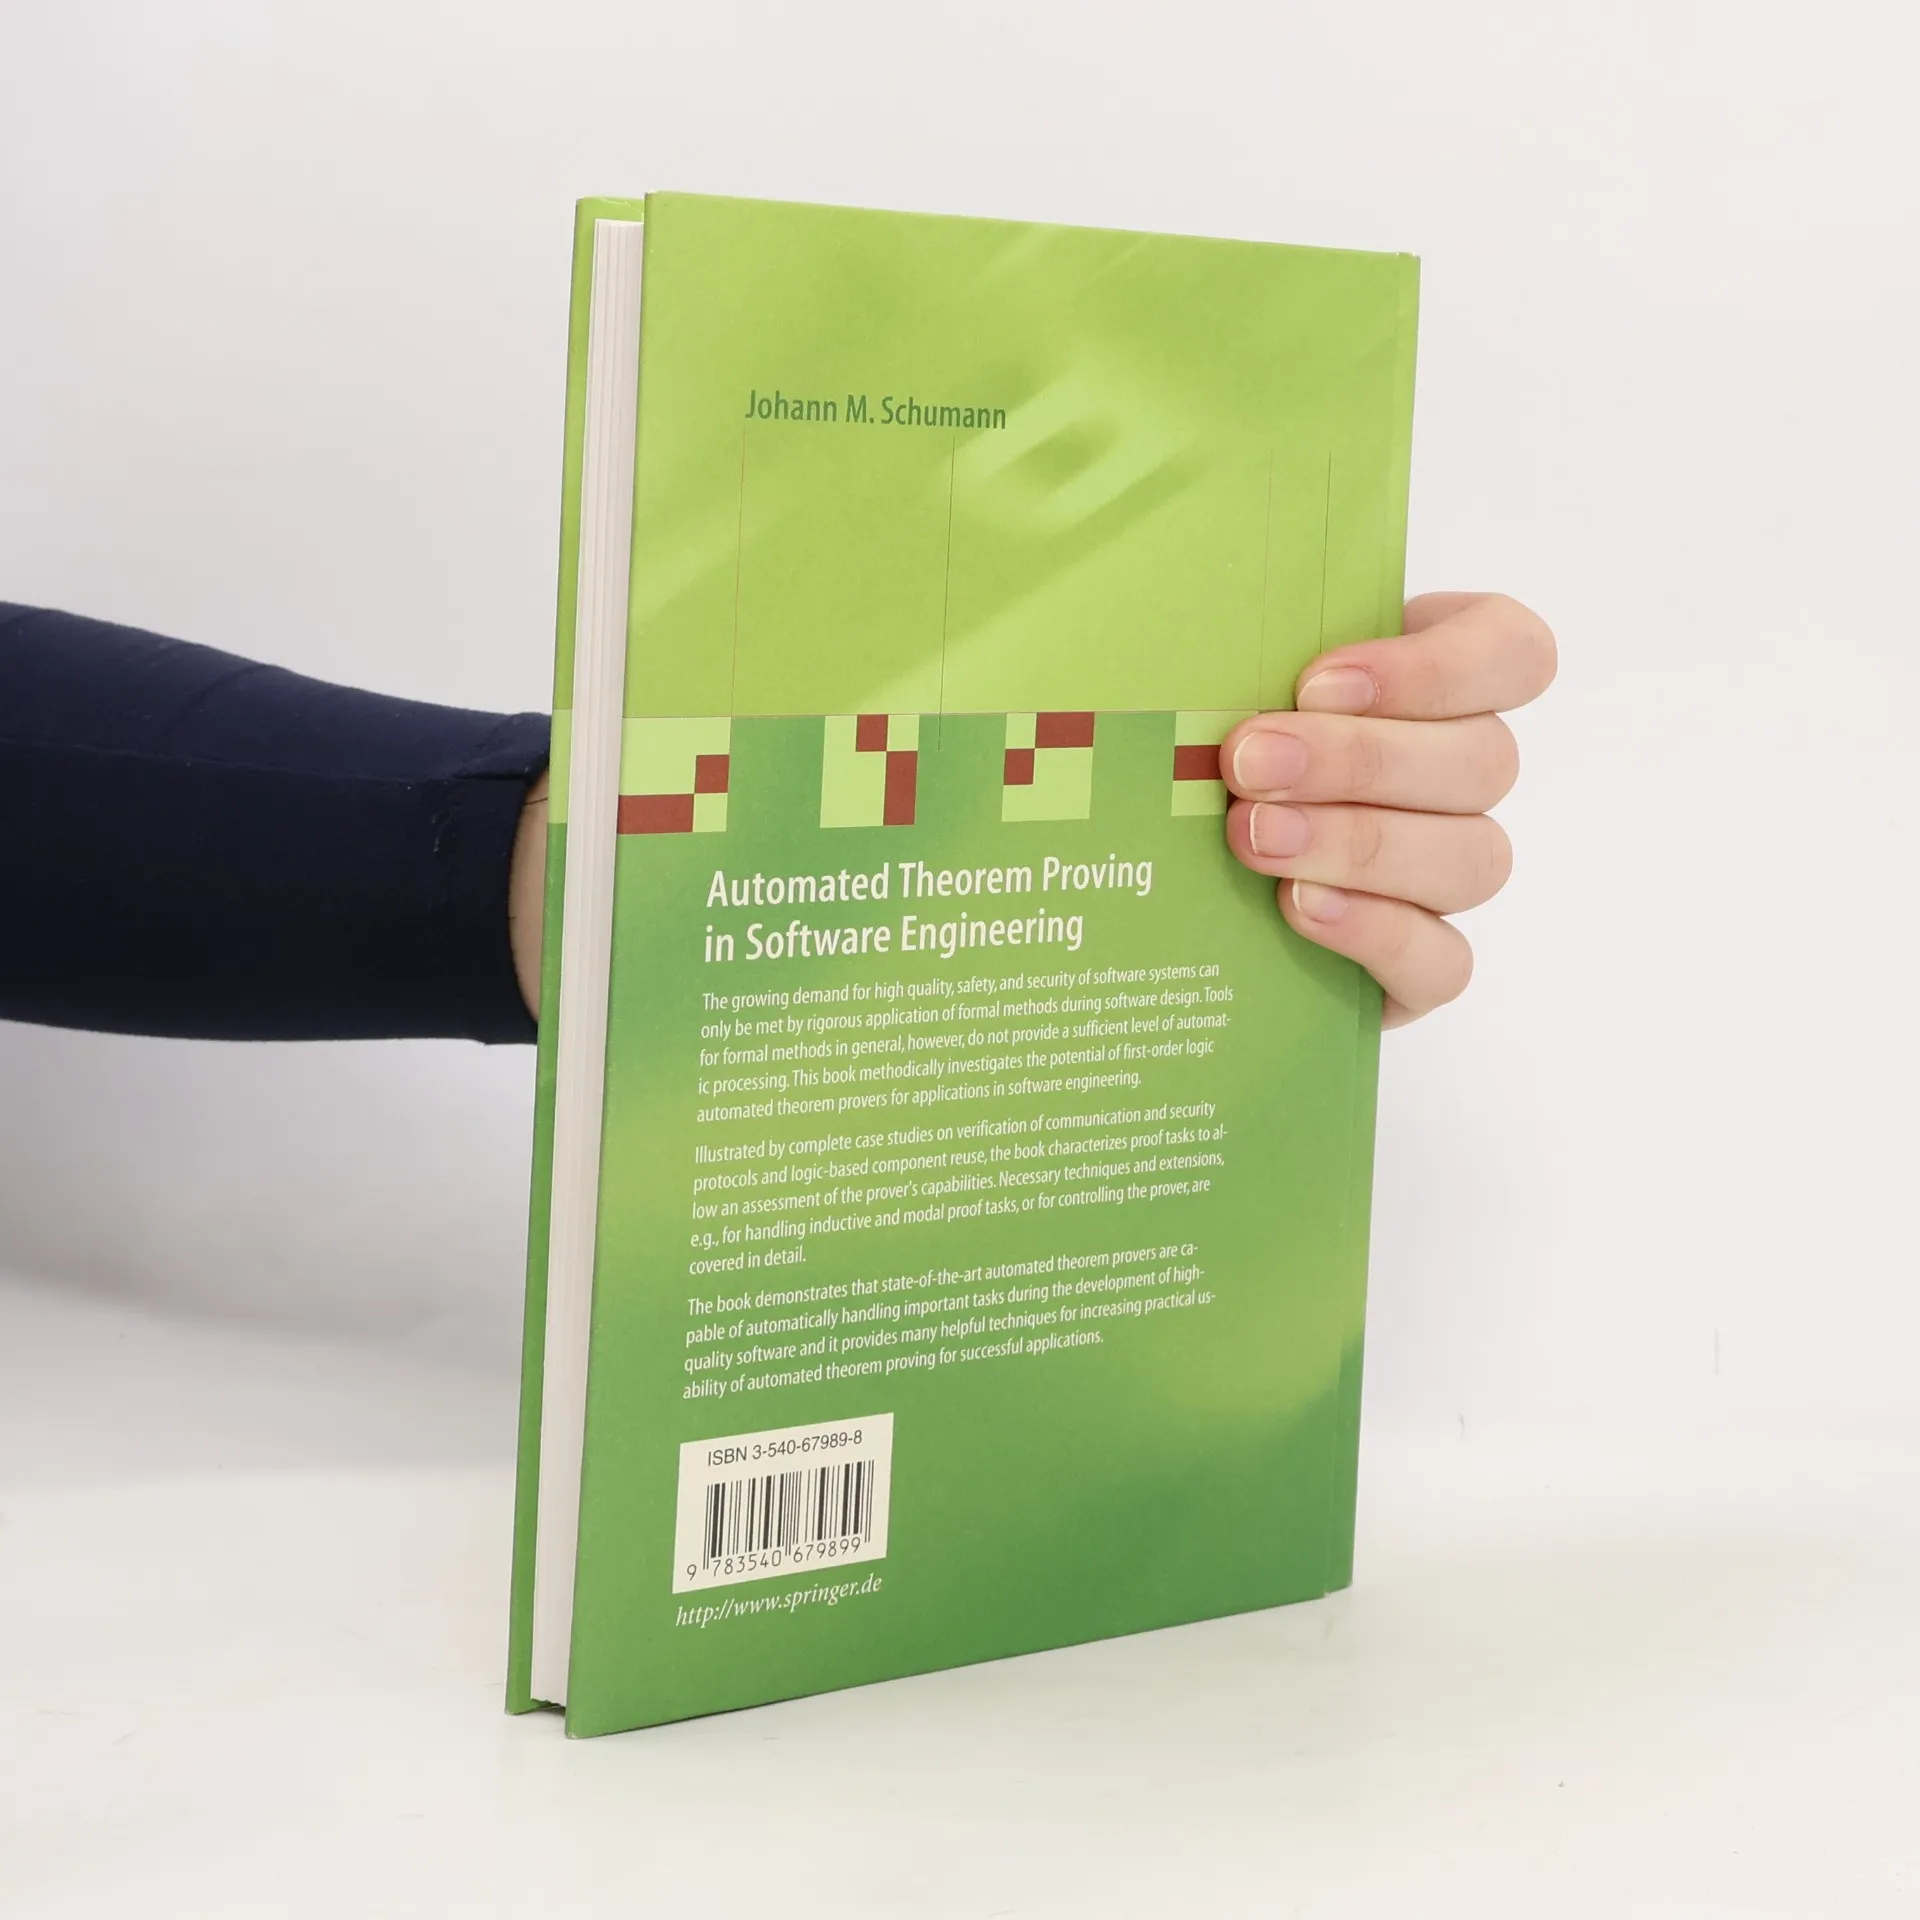
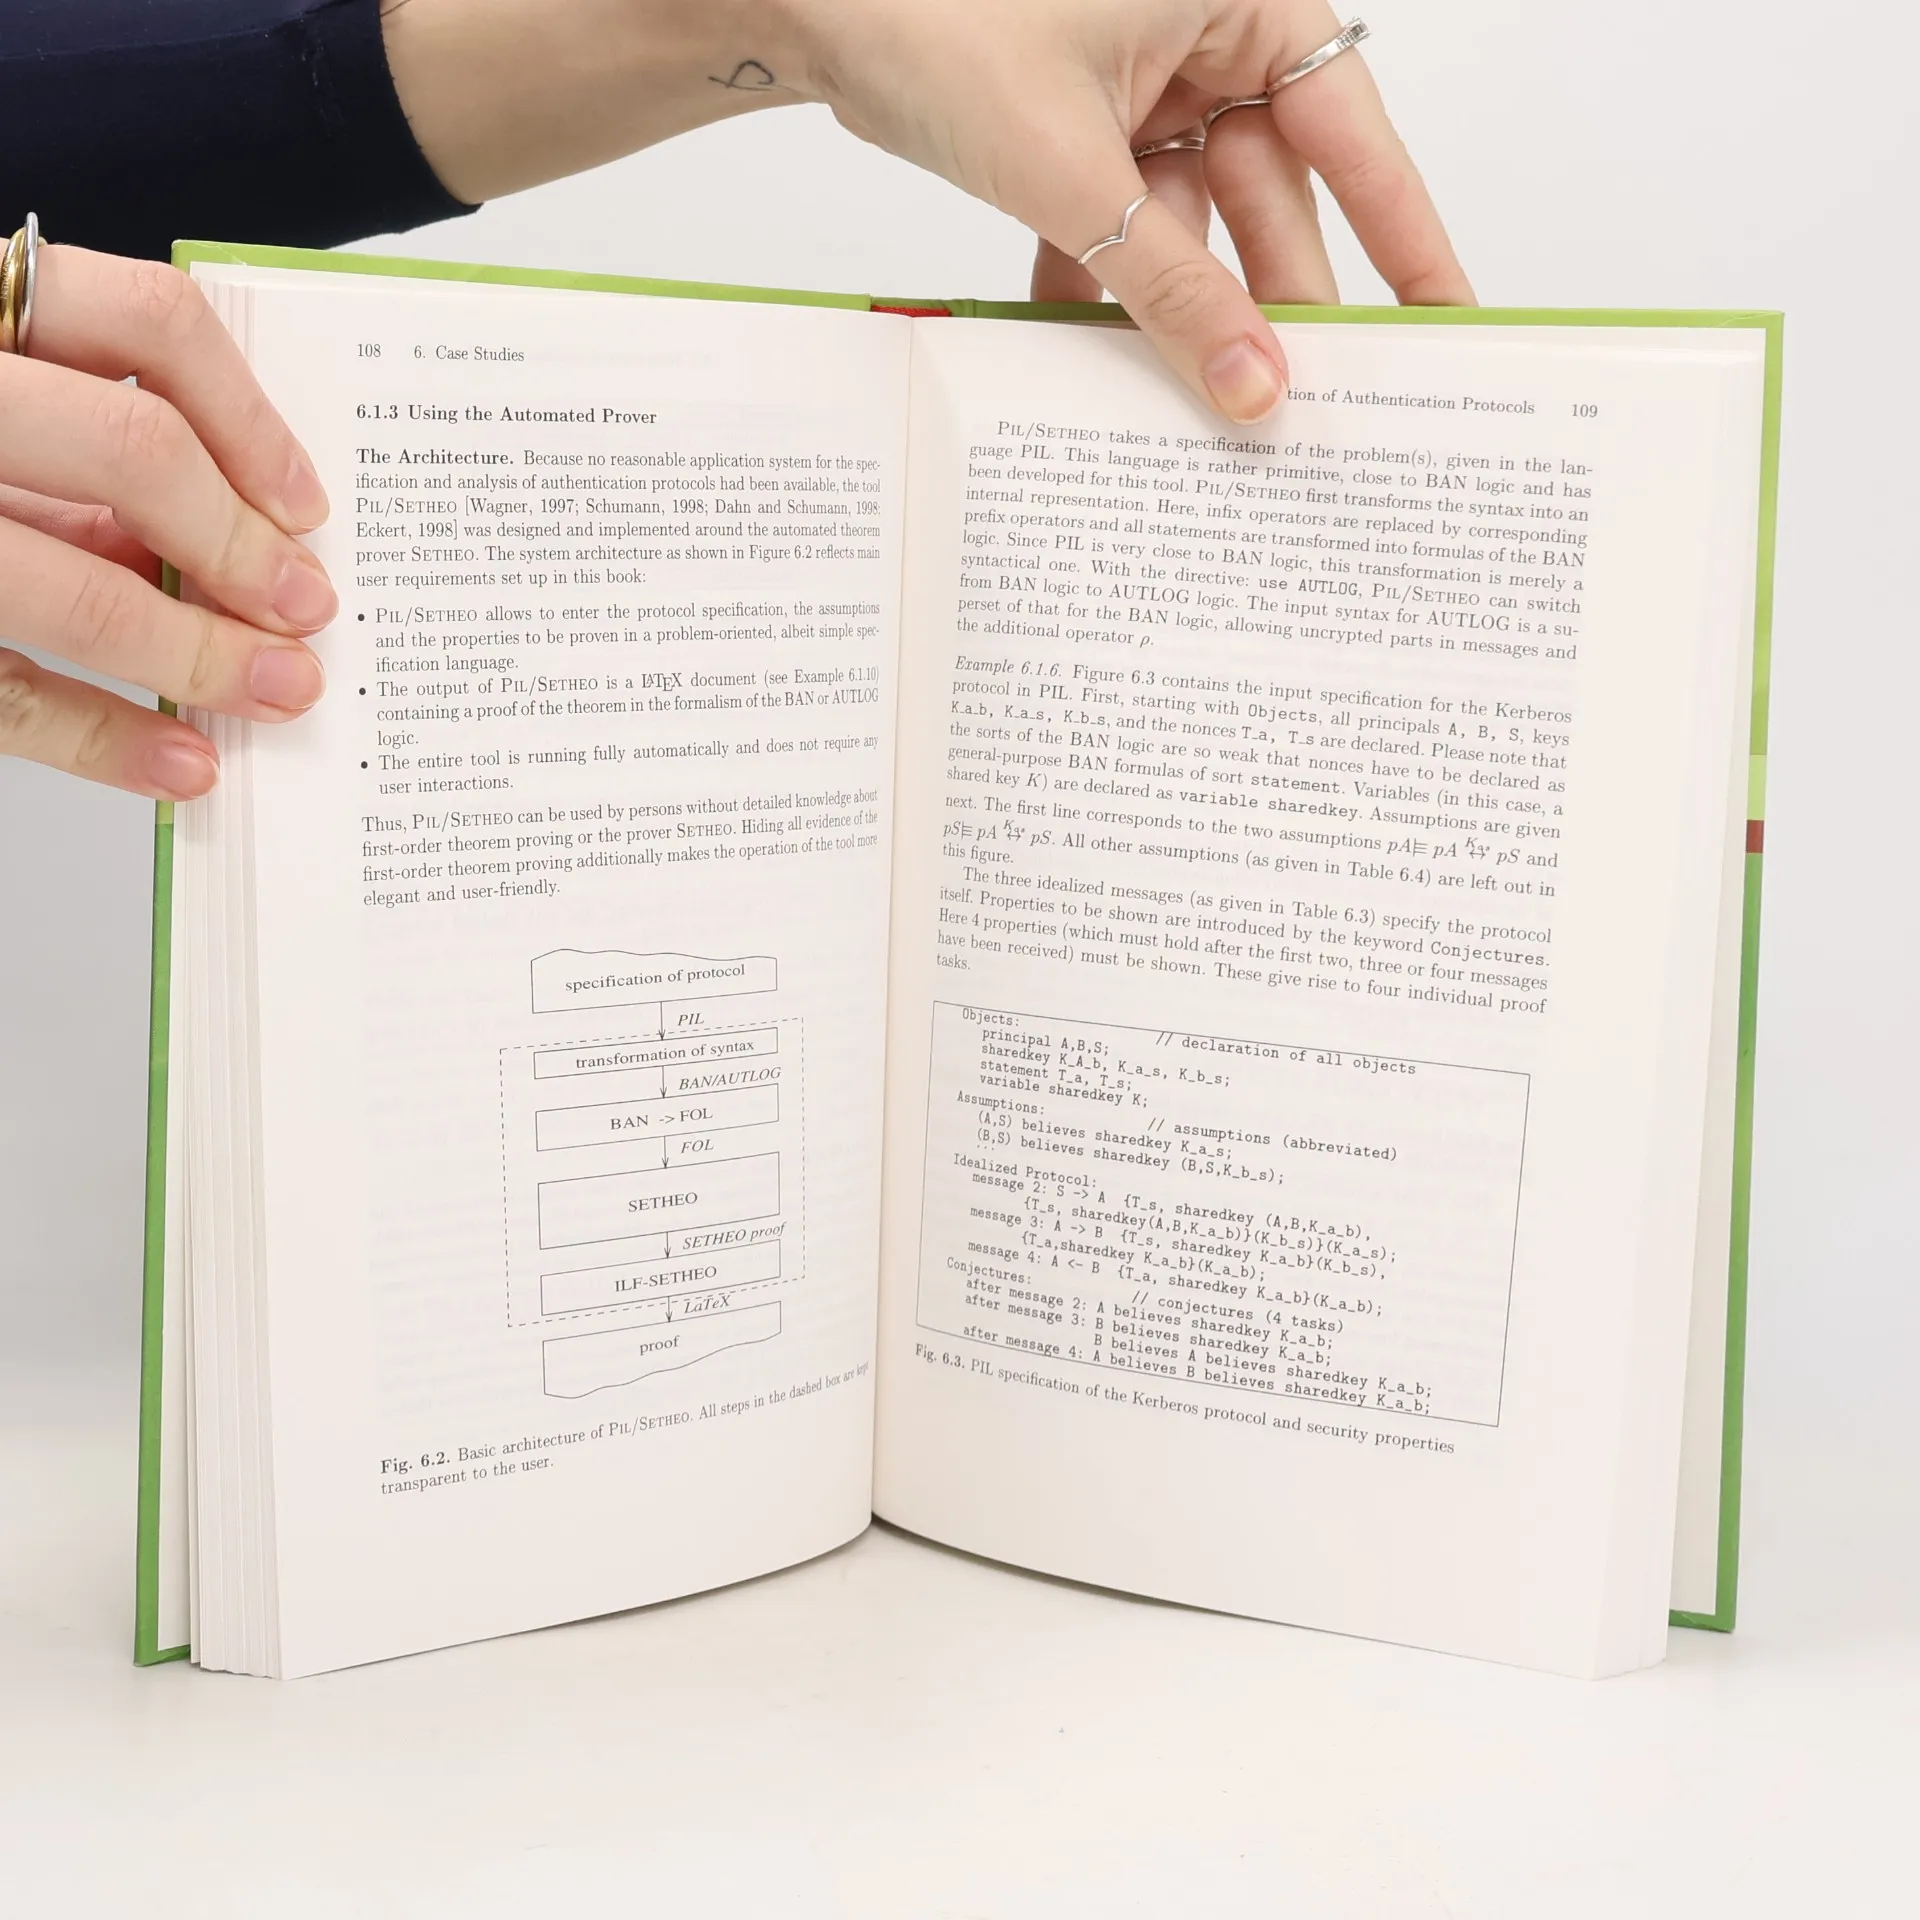
Automated Theorem Proving in Software Engineering
Parametry
- 228 stron
- 8 godzin czytania
Więcej o książce
Growing demands for the quality, safety, and security of software can only be satisfied by the rigorous application of formal methods during software design. This book methodically investigates the potential of first-order logic automated theorem provers for applications in software engineering. Illustrated by complete case studies on protocol verification, verification of security protocols, and logic-based software reuse, this book provides techniques for assessing the prover's capabilities and for selecting and developing an appropriate interface architecture.
Zakup książki
Automated Theorem Proving in Software Engineering, D. Loveland, Johann M. Ph. Schumann
- Język

- Rok wydania
- 2001
- Oprawa
- (twarda),
- Stan książki
- Dobry
- Cena
- 140,99 zł
Metody płatności
Nikt jeszcze nie ocenił.
- Tytuł
- Automated Theorem Proving in Software Engineering
- Język
- angielski
- Autorzy
- D. Loveland, Johann M. Ph. Schumann
- Wydawca
- Springer
- Rok wydania
- 2001
- Oprawa
- twarda
- Liczba stron
- 228
- ISBN10
- 3540679898
- ISBN13
- 9783540679899
- Seria
- Kategorie
- Tagi
- Architektura, Zachodnia Europa, Sztuczna inteligencja, Logika, Systemy operacyjne, Rozwój oprogramowania, Systemy informacyjne
- Opis
- Growing demands for the quality, safety, and security of software can only be satisfied by the rigorous application of formal methods during software design. This book methodically investigates the potential of first-order logic automated theorem provers for applications in software engineering. Illustrated by complete case studies on protocol verification, verification of security protocols, and logic-based software reuse, this book provides techniques for assessing the prover's capabilities and for selecting and developing an appropriate interface architecture.